Writing
Blog
Notes on what I build, break and learn along the way. Software and frontend engineering, performance, accessibility and security, plus the parts of the job that never show up in a diff, like leading a team and explaining a technical decision to people who don't write code. Posts live here first and are syndicated elsewhere.
10 postsLast published RSS feed
 Latest6 min read
The AI endpoint that charges you money when somebody abuses it
Abuse of a normal endpoint costs you capacity. Abuse of an endpoint that calls a model costs you money per request while everything looks healthy. Four controls, and the quota bug that charges you for every rejection.
- security
- ai
- appsec
- webdev
 Featured9 min read
Your coding agent runs as you. So does everything you install into it.
A skill passed every scanner, and the scanners were right at the moment they looked. Why the artefact you review and the instruction that runs are two different objects, and how to inventory what your coding agent can actually reach.
- security
- ai
- appsec
- webdev
 Featured8 min read
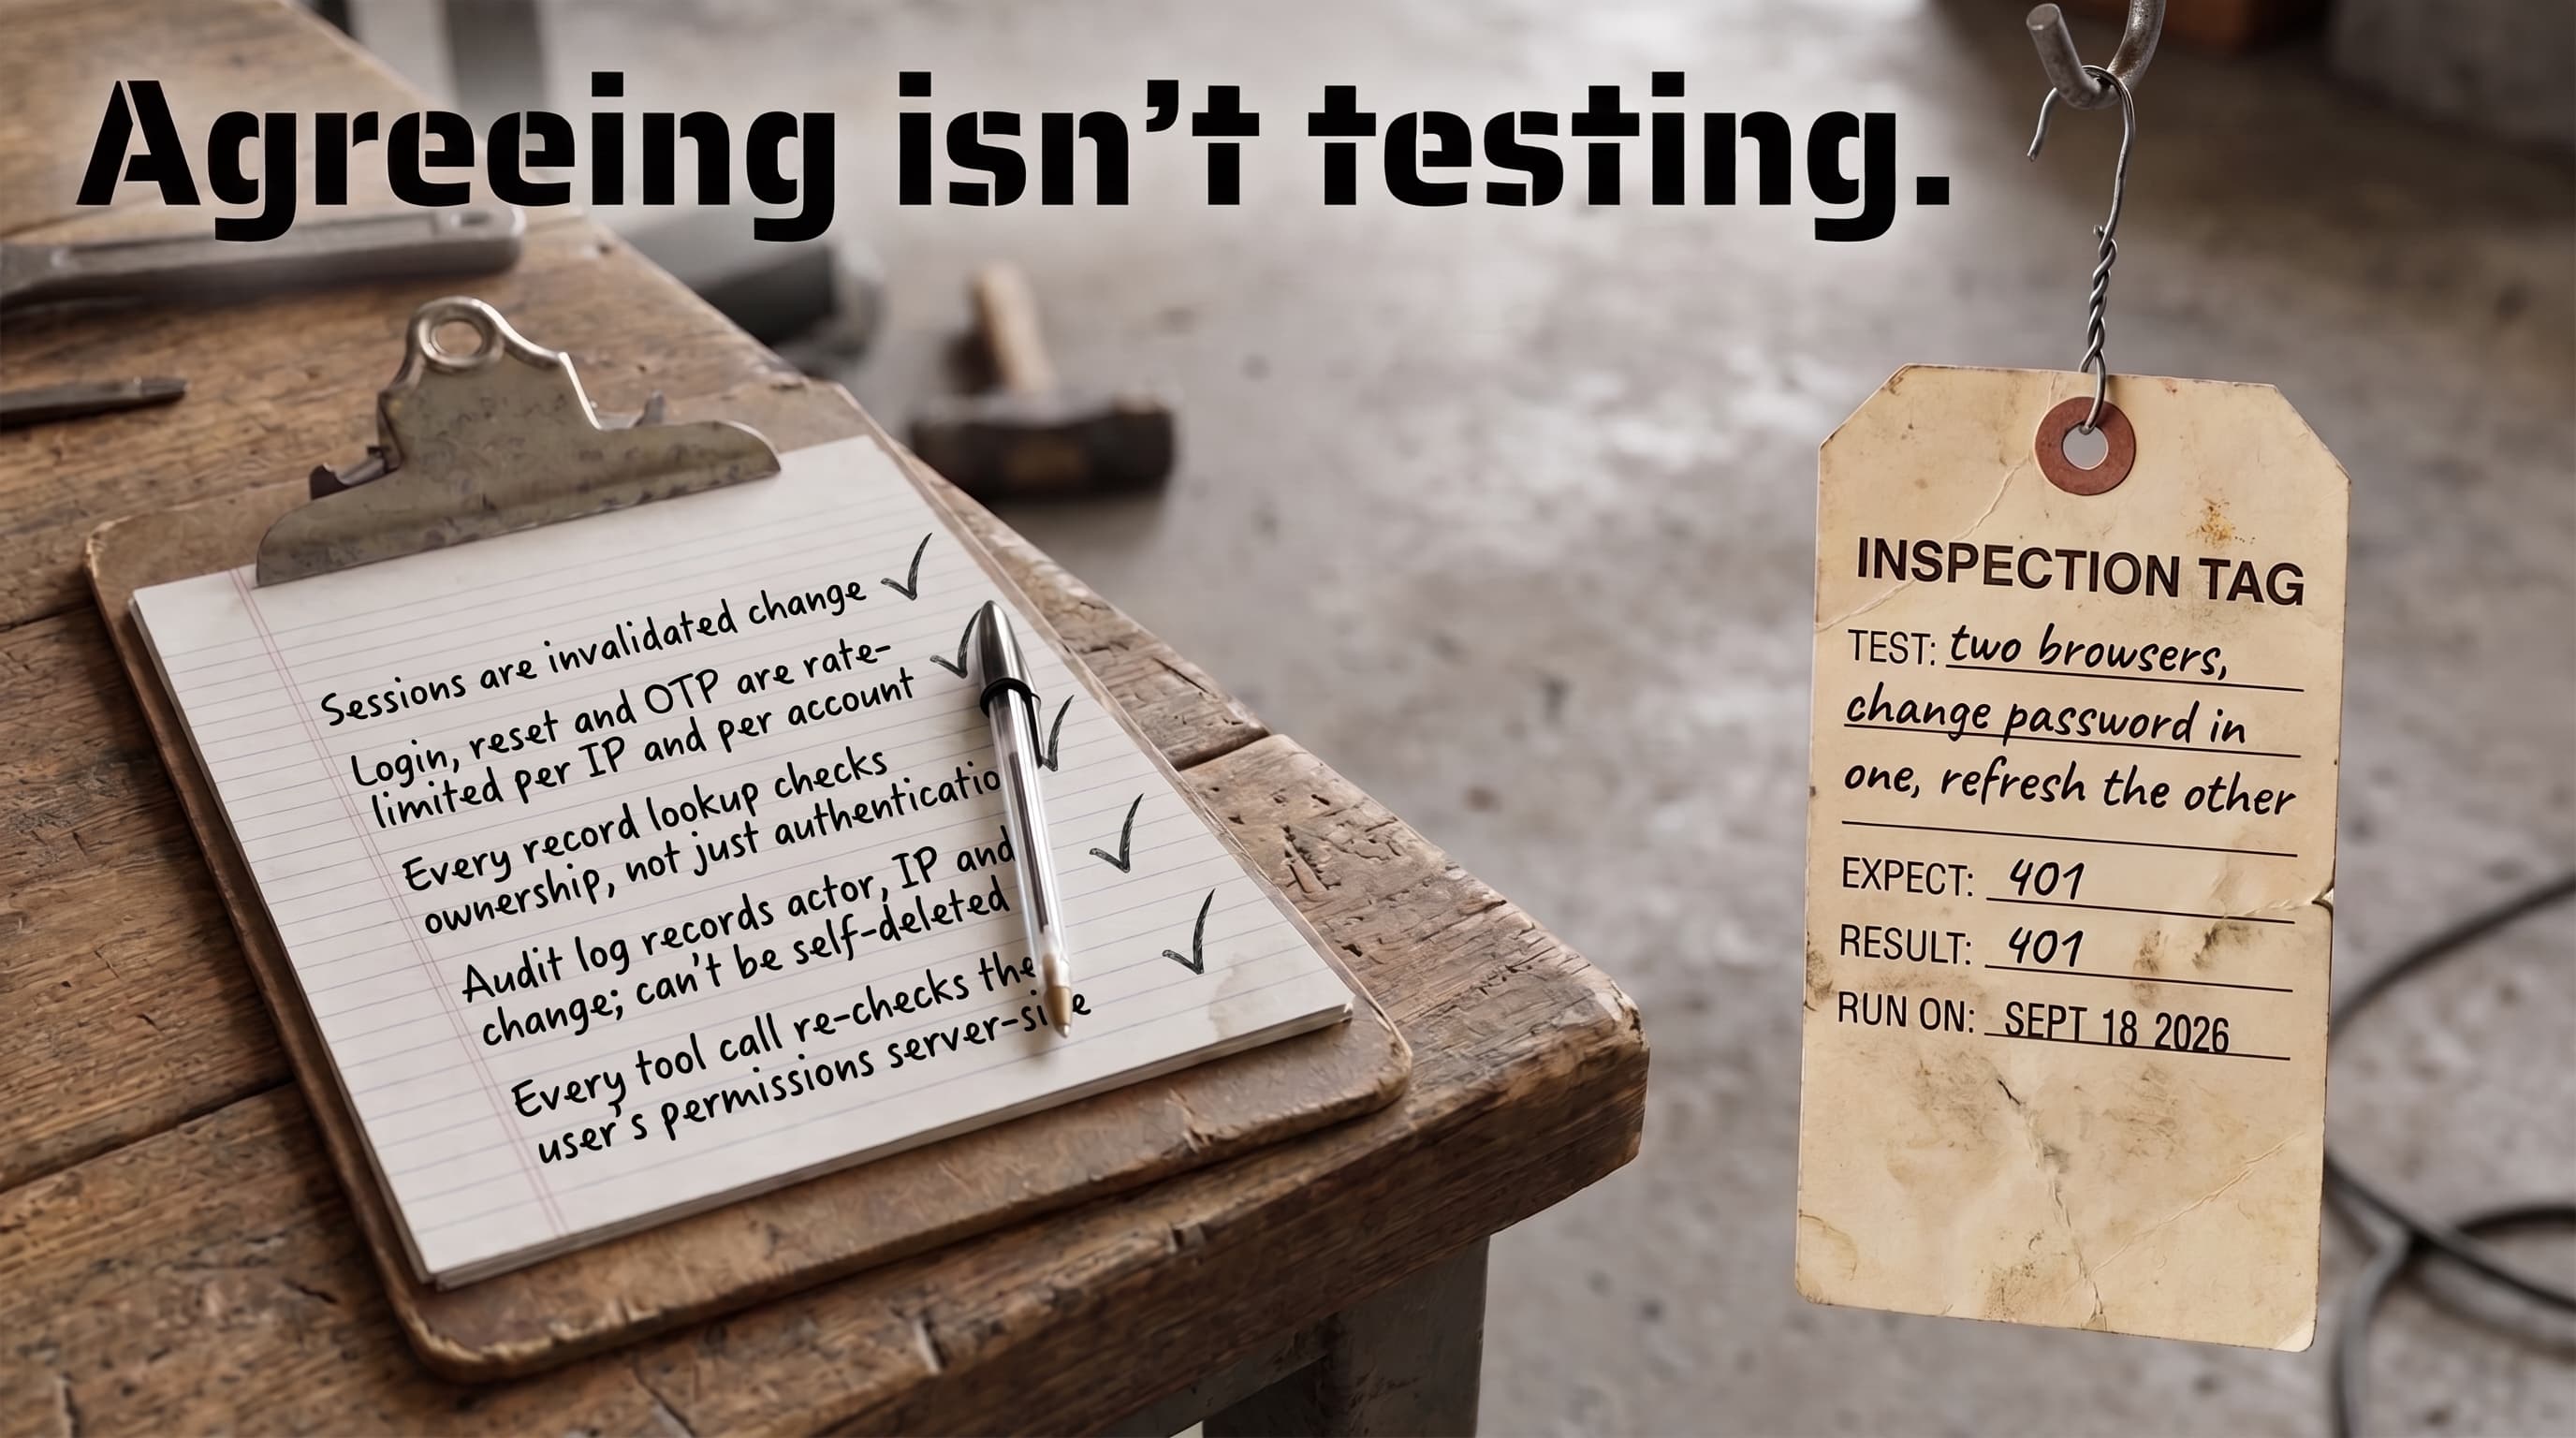
A security checklist my coding agent has to run
Most security checklists say what should be true and never get tested. Here is what happened when every item was rewritten as something you run, and packaged as a skill a coding agent loads before it writes the code.
- security
- appsec
- ai
- webdev
 Featured11 min read
What my WAF actually blocked, and what my app already stops on its own
I ran 26 attack payloads against a local replica of a production app with ModSecurity on and off. It blocked 12: five my app already rejected, and seven it stopped a step earlier than the app's own defences. The class behind most real breaches never showed up in either column.
- security
- webdev
- devops
- cybersecurity
 12 min read
October brought the awareness after all
Cybersecurity Awareness Month 2026 brought PHP2Shell, an exploited BeyondTrust zero-day and two critical Next.js RCEs. My dependency audit stayed green for eight days while the Next.js fix sat on npm, and on a repository I had not patched yet, Dependabot was still silent days after the database caught up.
- security
- webdev
- devops
- cybersecurity
 9 min read
The three questions you get asked at 2am
When something goes wrong, three questions get asked and most teams cannot answer any of them. Why application logs are not an audit trail, how the record becomes a liability, and five questions a non-technical leader can ask about it.
- security
- appsec
- devops
- webdev
 12 min read
A pentest lab on Apple Silicon (and what a frontend dev did with root)
Most lab guides assume an Intel machine and VirtualBox, which falls apart on an M-series Mac. Here is the one insight that fixes it, the seven phases of a pentest walked end to end against a real target, and the part where a frontend developer got hold of root and could not resist writing CSS with it.
- cybersecurity
- security
- pentesting
- applesilicon
 9 min read
Prompt injection is an authority problem, not a wording problem
Most prompt injection defences are a sentence in a system prompt, which asks the thing being attacked to defend itself. The alternative is architectural: the model never holds authority, and every tool call is re-checked against the user's own permissions.
- security
- ai
- appsec
- webdev
 7 min read
Ethical hacking is not a toolset, it is a mindset with a permission slip
Hacker, ethical hacker and penetration tester are not the same thing, and one of the differences is an invoice versus a criminal record. The mindset, the seven-stage method, and the black, grey and white box styles, laid out plainly.
- cybersecurity
- security
- appsec
- penetrationtesting
 6 min read
From zero to tech lead: what the AltSchool year actually taught me
No background in tech, a repo that emptied itself two hours before a deadline, and a diploma in frontend engineering at the end of it. The year I spent at AltSchool Africa, and what it led to.
- career
- beginners
- webdev
- frontend