Security
I break what I build
Application security from the builder's side. I build software secure by default, then take it apart in a lab I control to see what actually holds, and write down what I find.
Rules of engagement
- 01PermissionI only test what I own or have written permission to test.
- 02ScopeI stay inside what was agreed, even when something interesting sits just past it.
- 03ReportEvery test ends in a written report: what I found, why it matters, and how to fix it.
Google Cybersecurity Professional CertificateGoogleVerify on CredlyCoursera record
- GitHub Actions
- Semgrep
- Trivy
- Gitleaks
- GitHub CLI
- jq
- ModSecurity
- OWASP CRS
- NGINX
- Docker
- Juice Shop
- Python
- curl
- UTM
- QEMU
- Kali Linux
- Ubuntu Server
- nmap
- searchsploit
- OpenVAS/GVM
- Hydra
- Metasploit
- John the Ripper
- Wazuh
- Suricata
- VirusTotal
- Emerging Threats rules
- GoPhish
- Mailpit
- Go
- CVE-2011-2523
- CVE-2019-14287
6 labs
Labs
Each one goes end to end and names the control that would have stopped it.
- 01
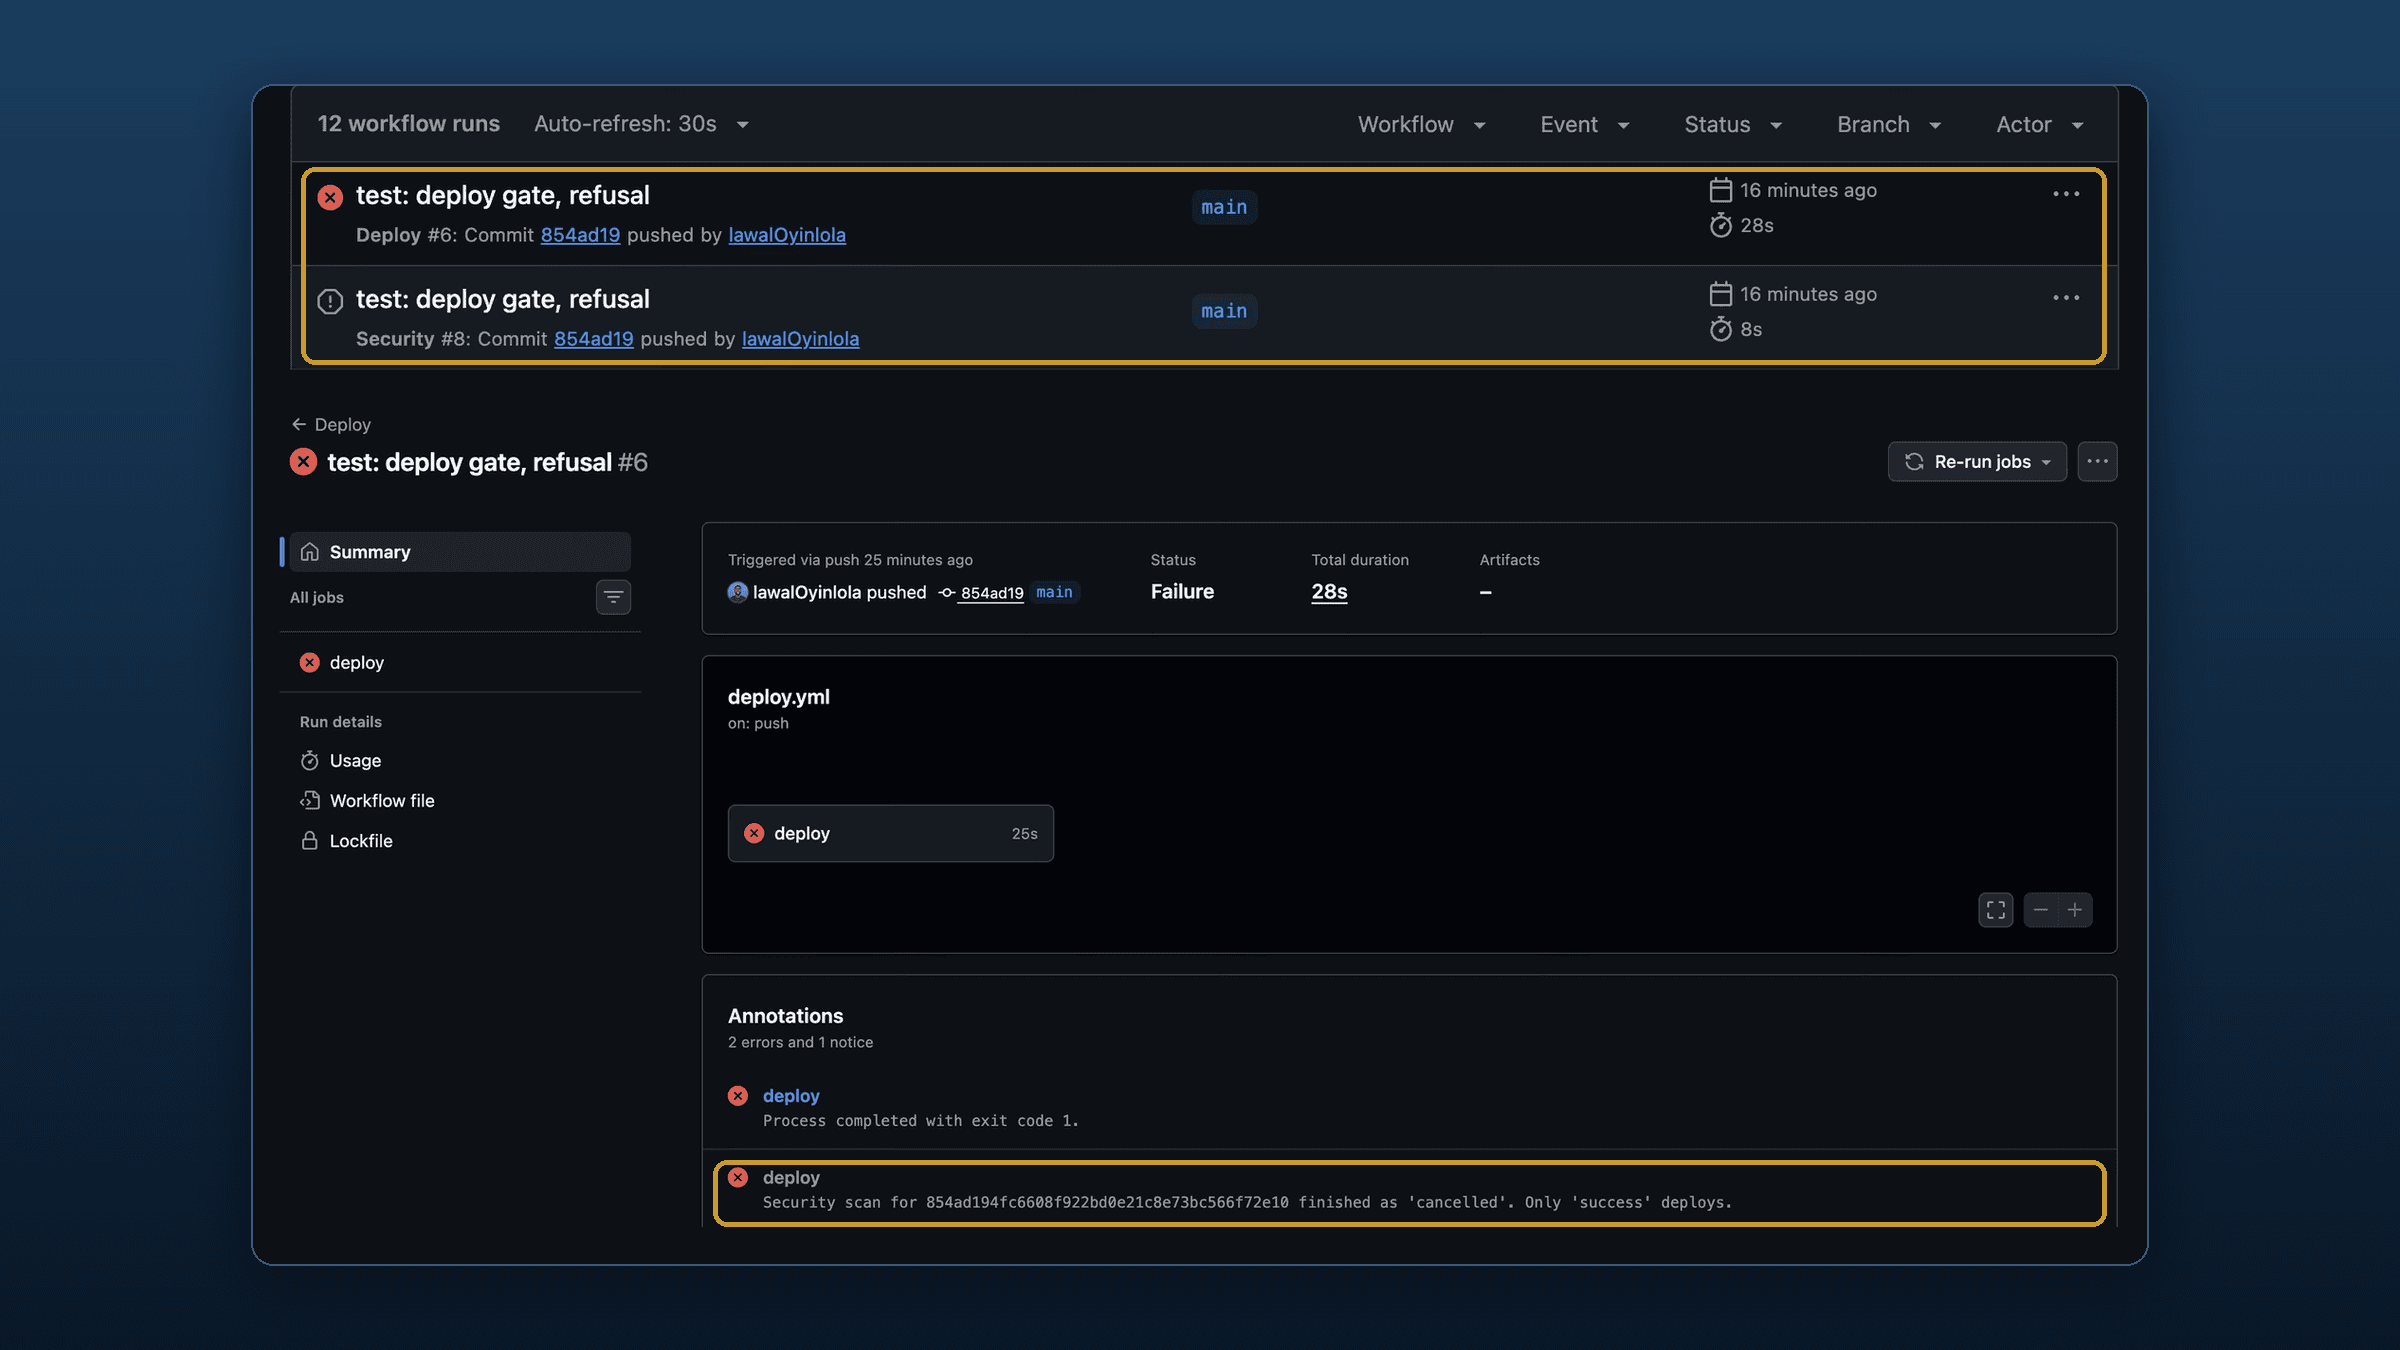 The CI/CD Security Lab: Scanning, Policy and a Deploy Gate That Fails ClosedSelf-hostedMediumA Next.js + NestJS web app
- 02
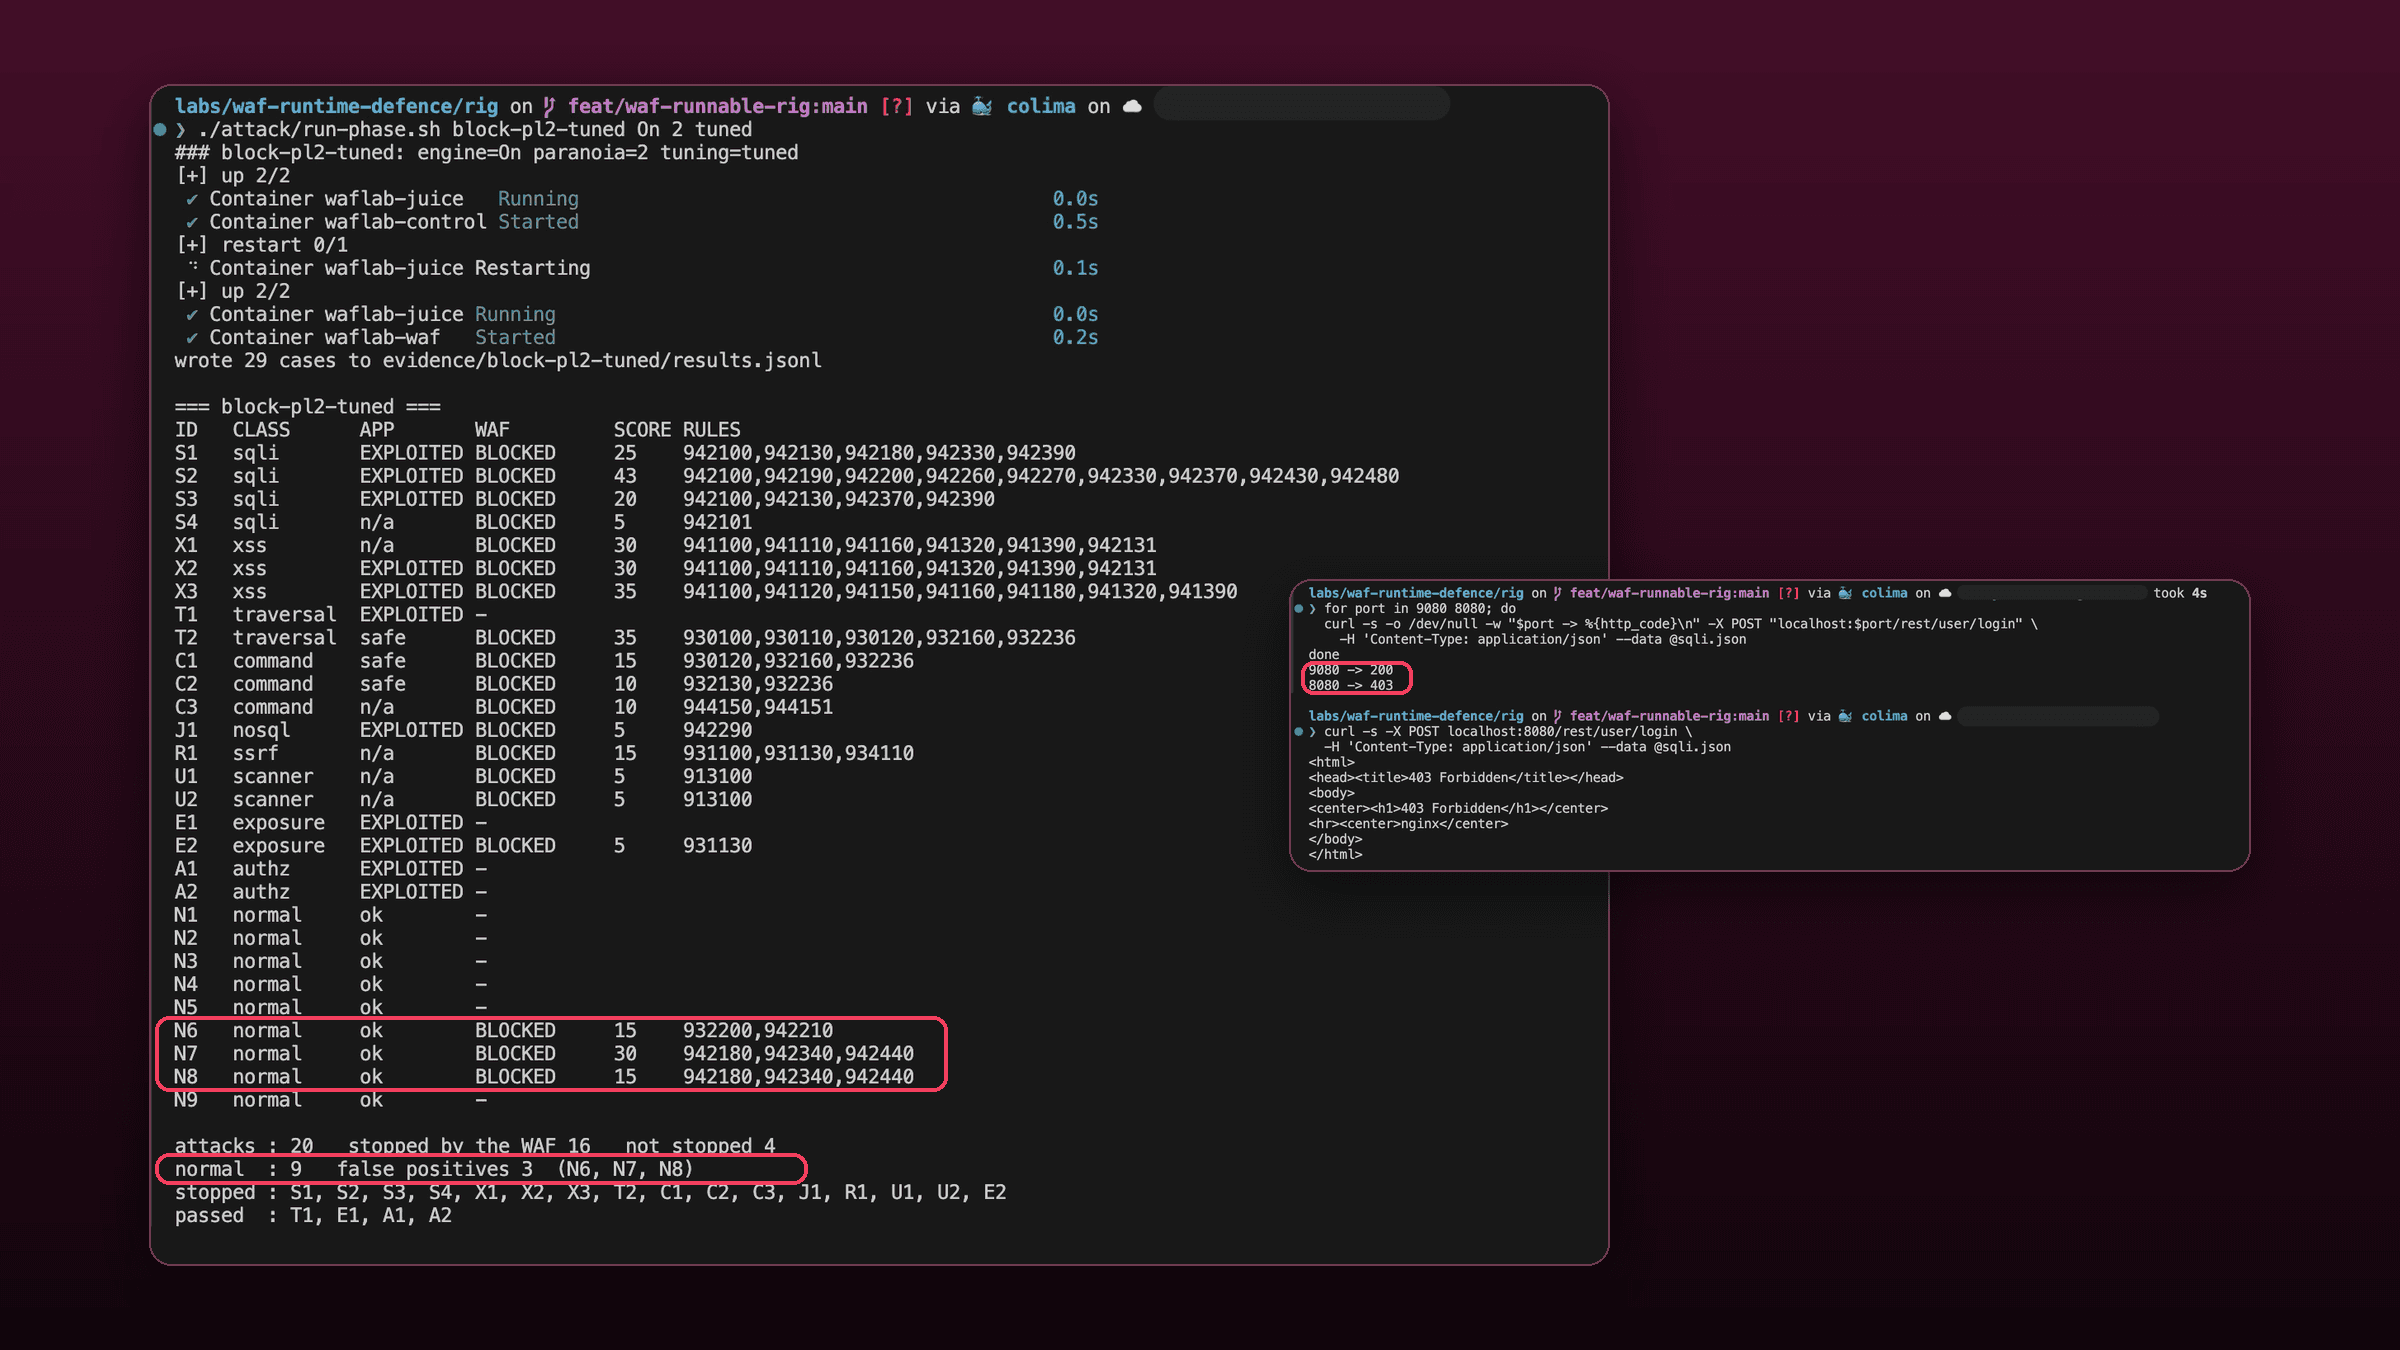 The WAF Lab: ModSecurity and the Core Rule Set, Measured Against a ControlSelf-hostedMediumOWASP Juice Shop
- 03
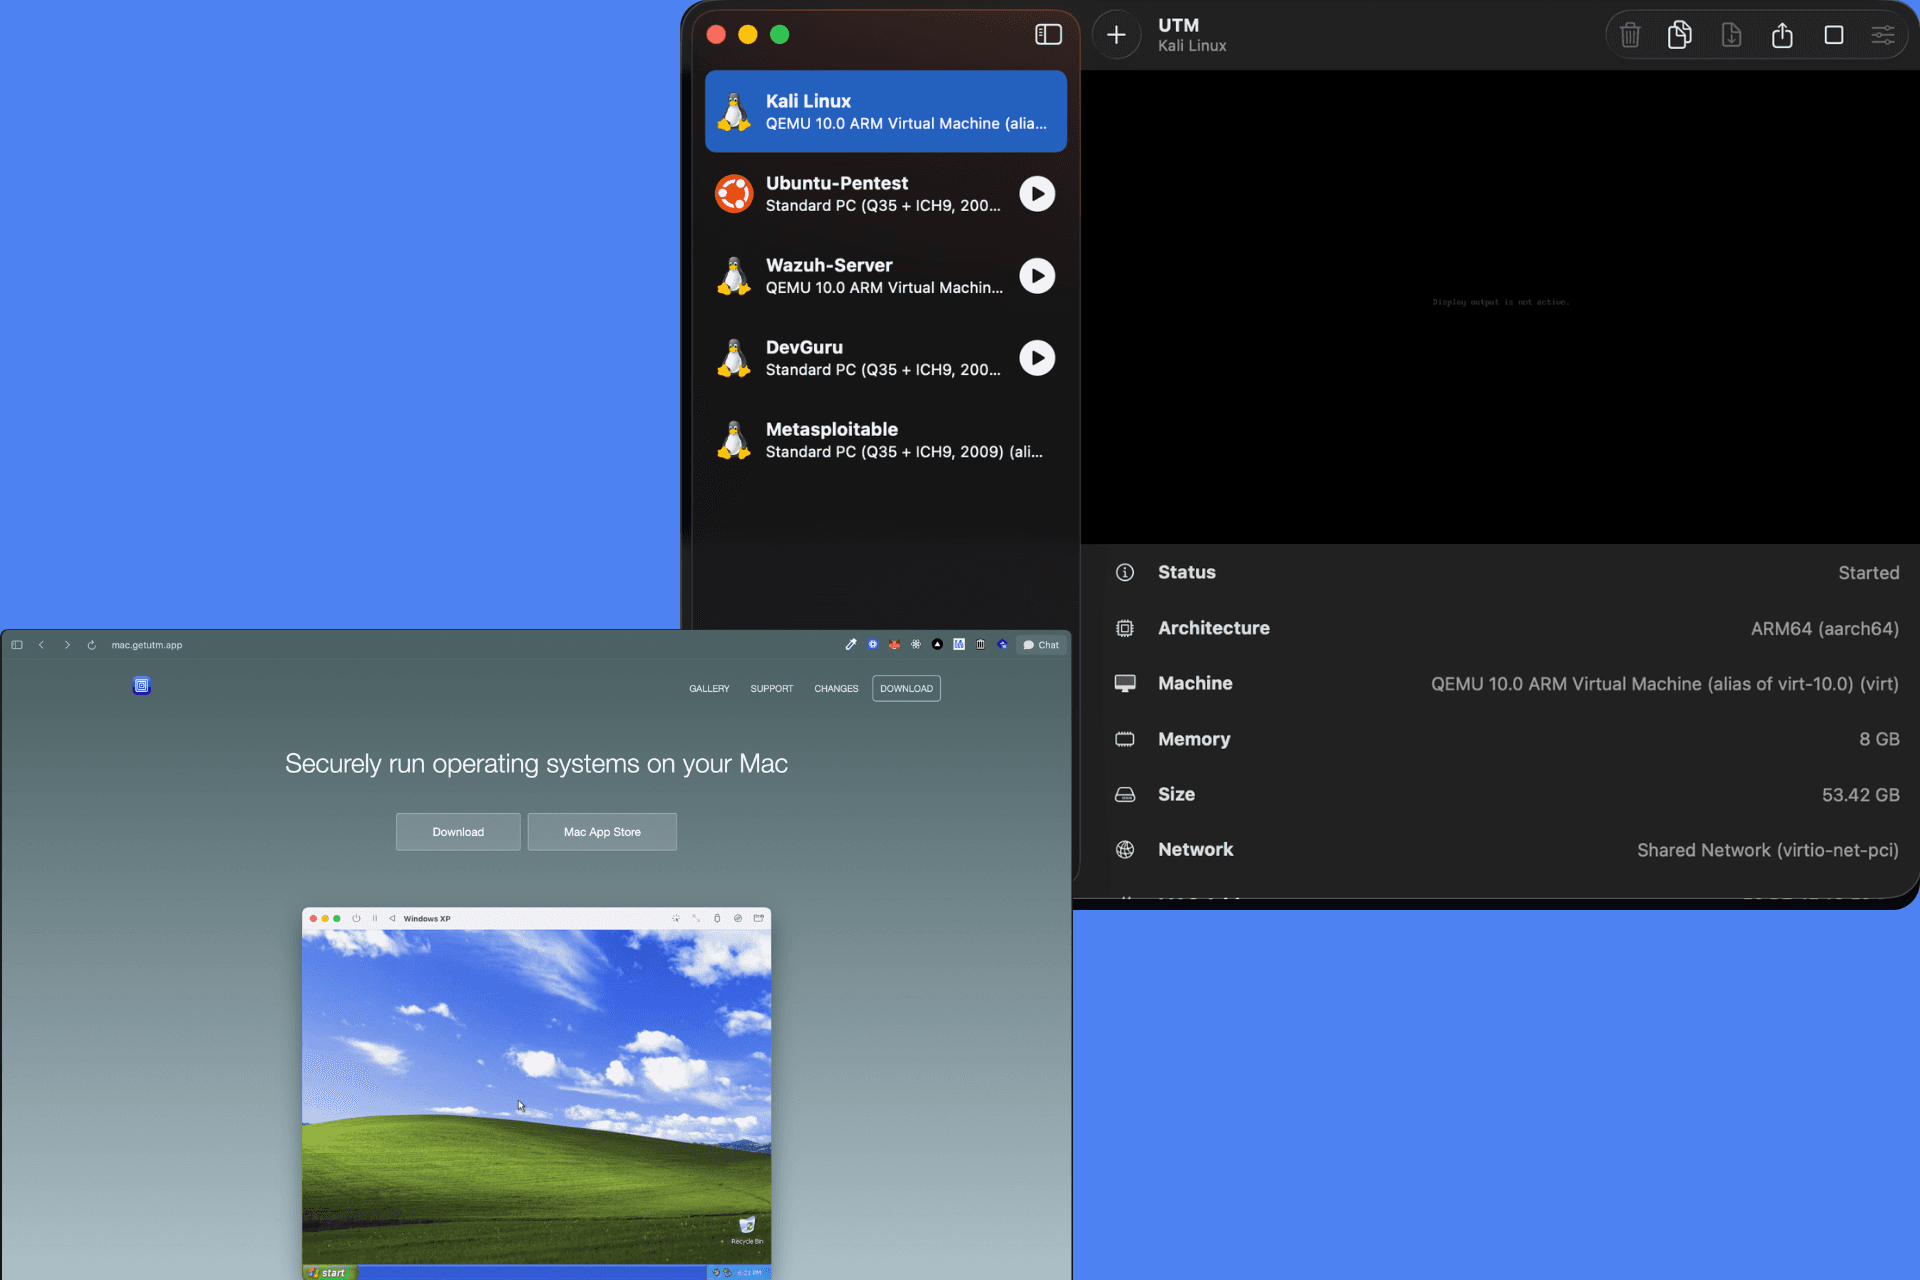 The Foundation Lab: One Security Lab Environment on Apple SiliconSelf-hostedEasyLocal VM lab
- 04
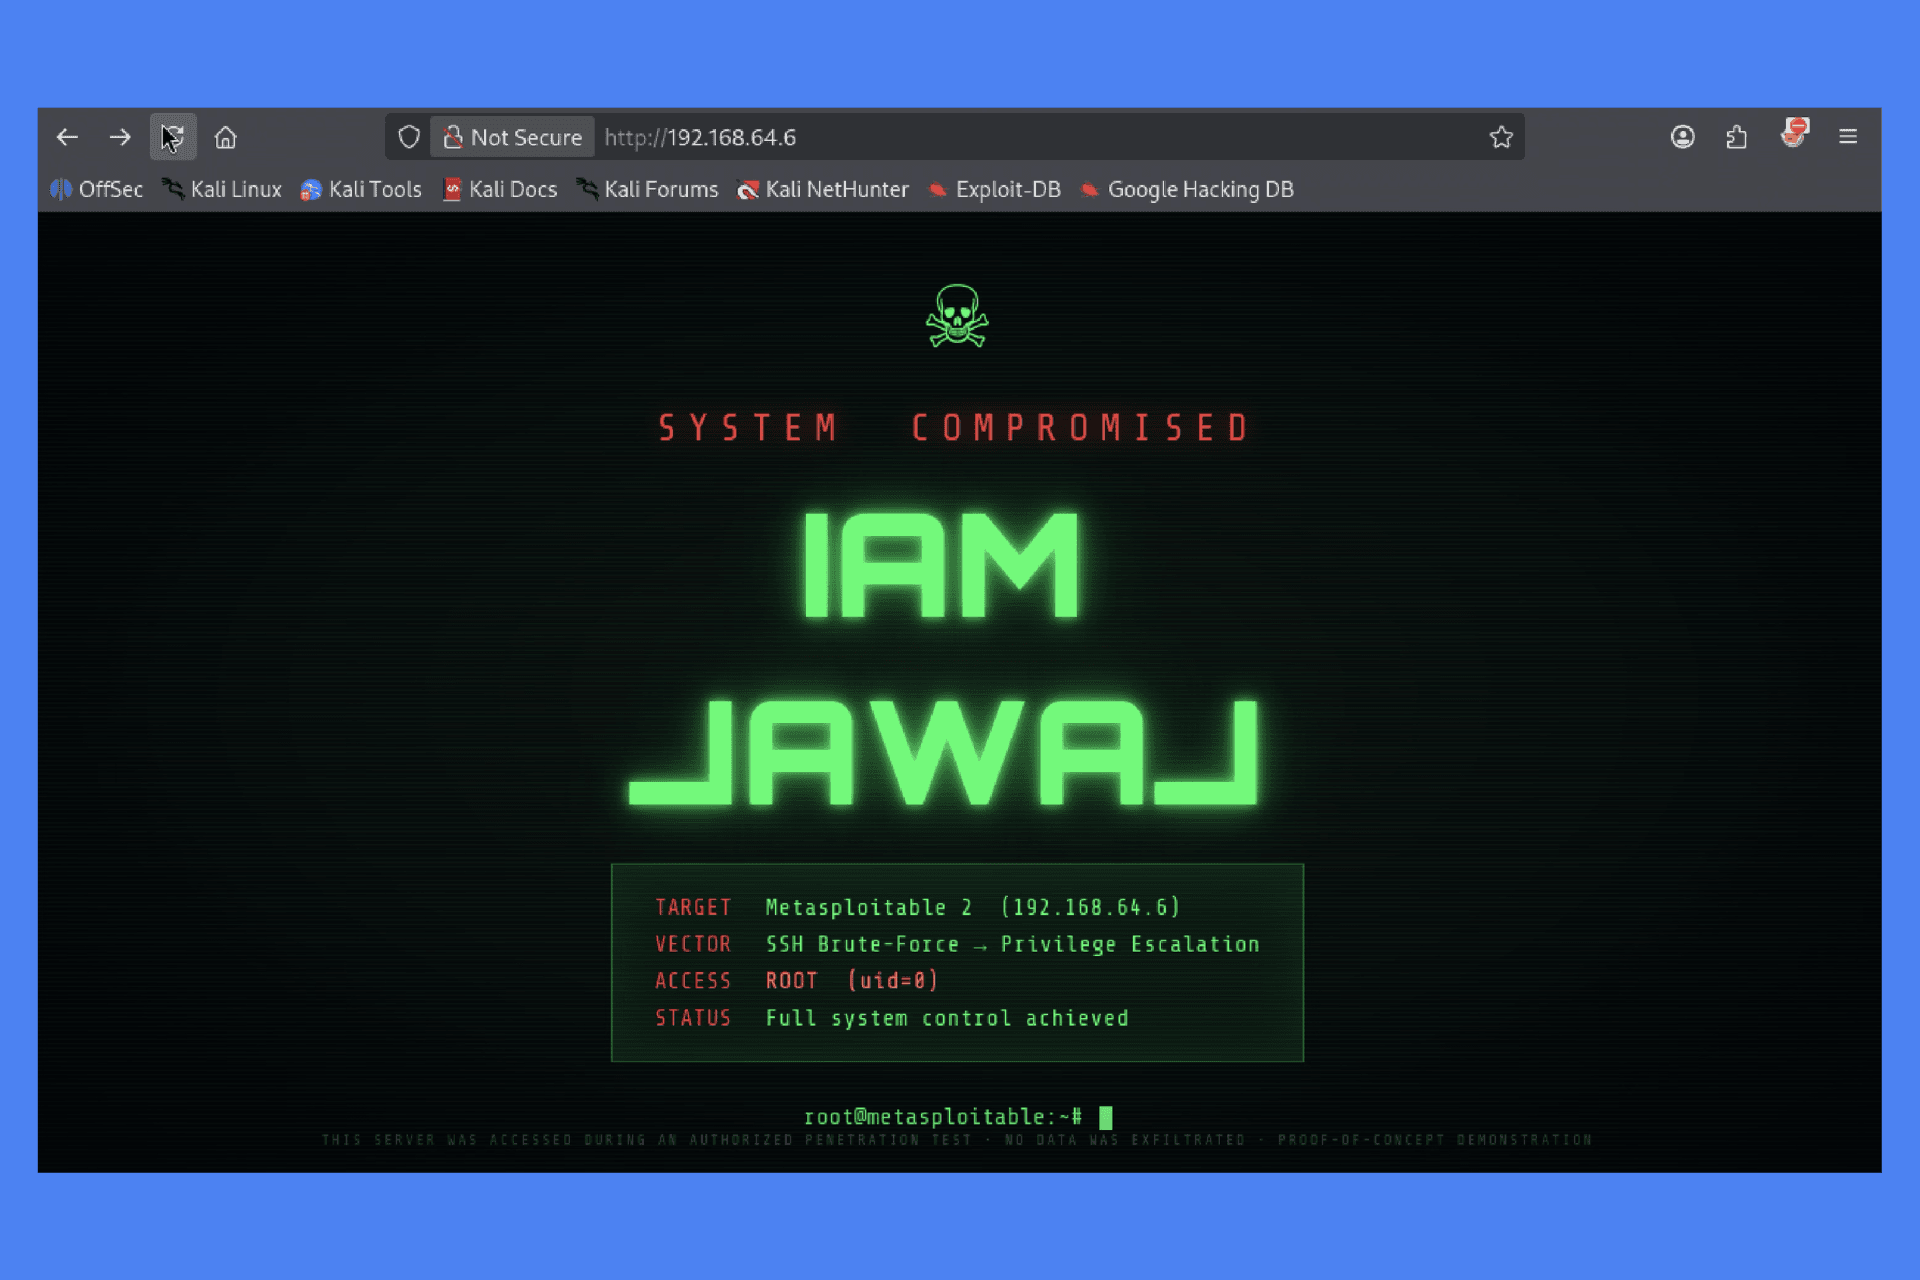
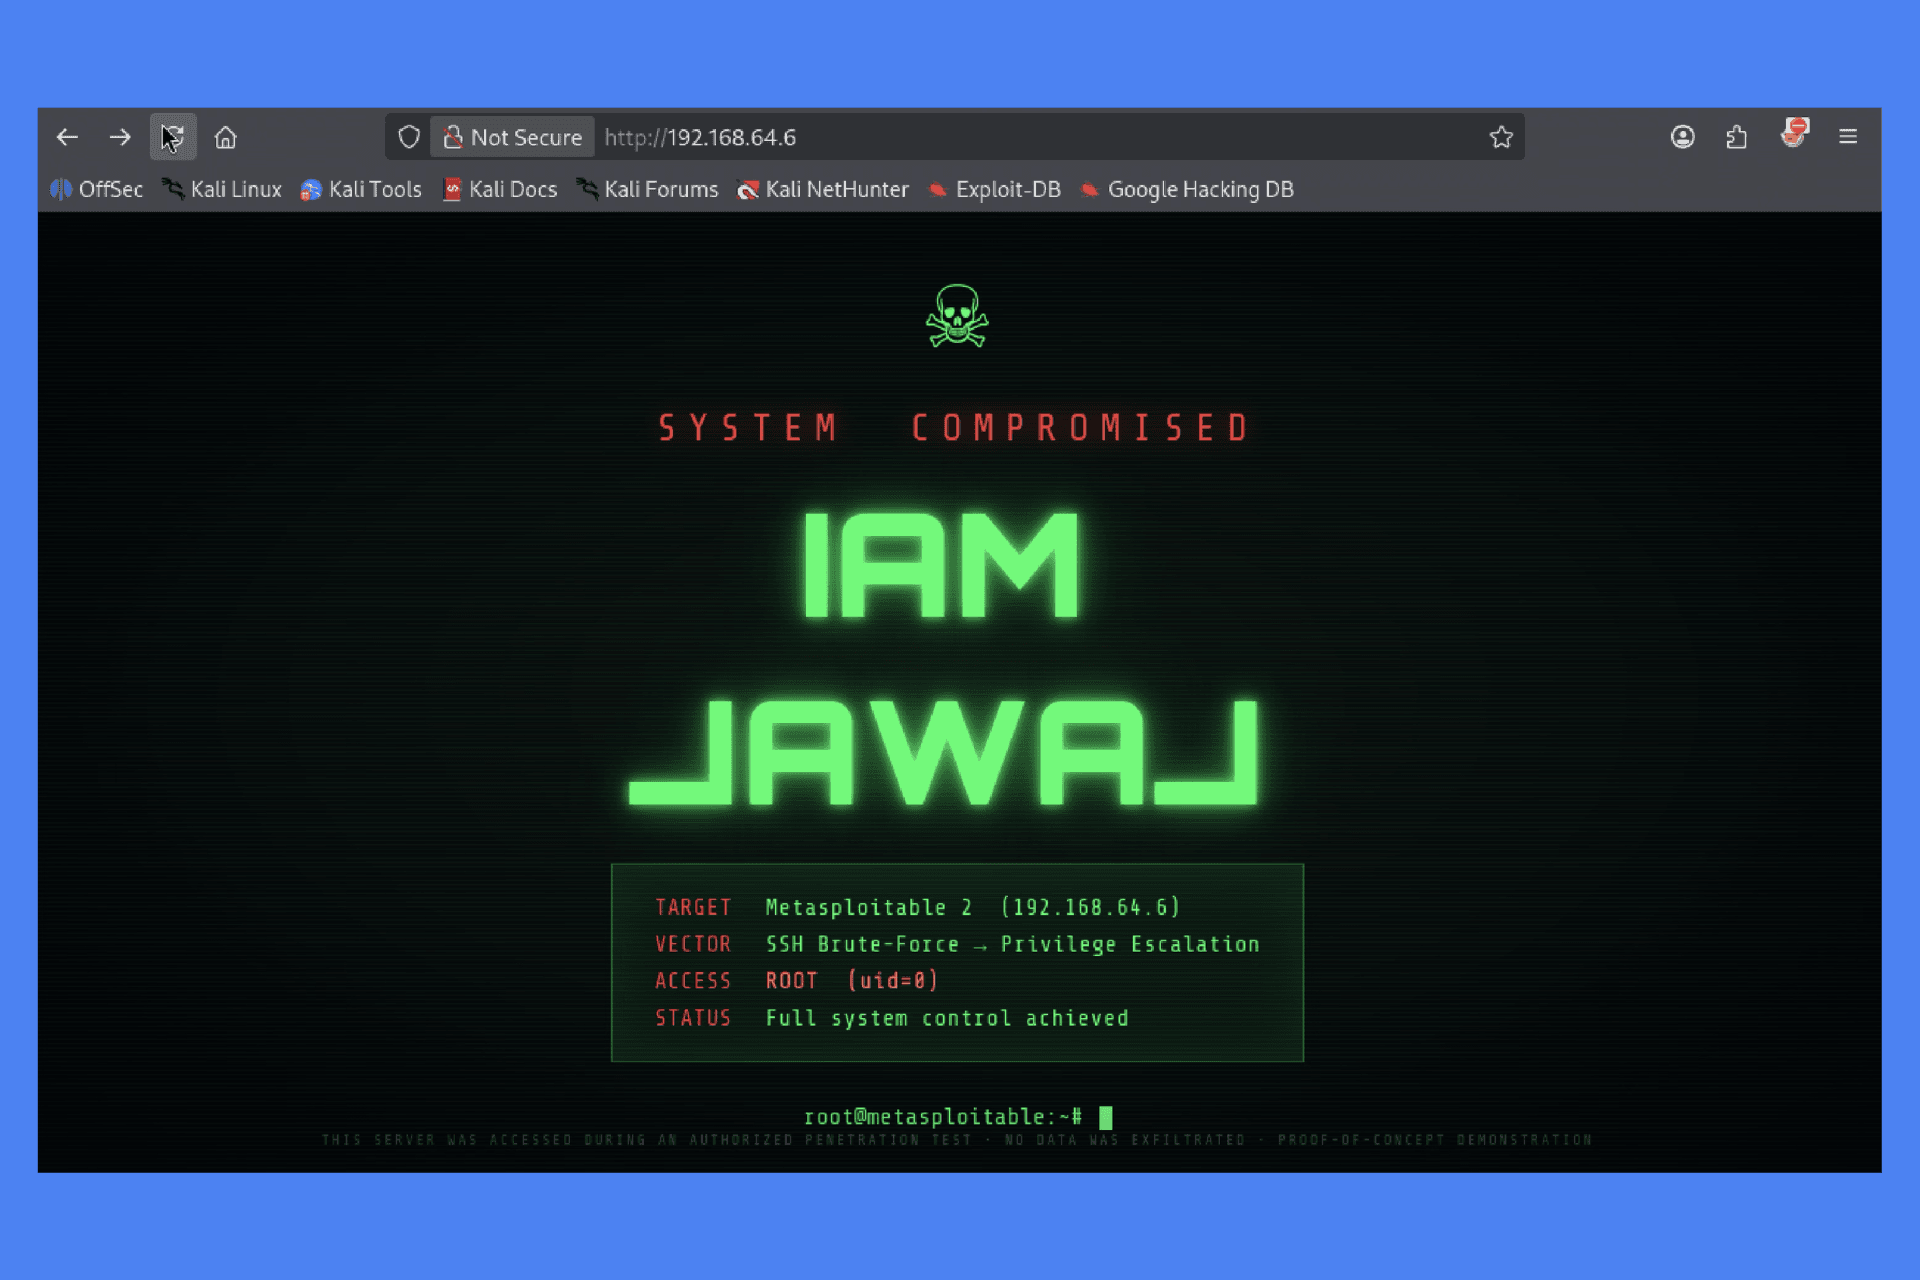 Building a Pentest Lab on Apple Silicon: A Complete GuideSelf-hostedEasyMetasploitable 2
- 05
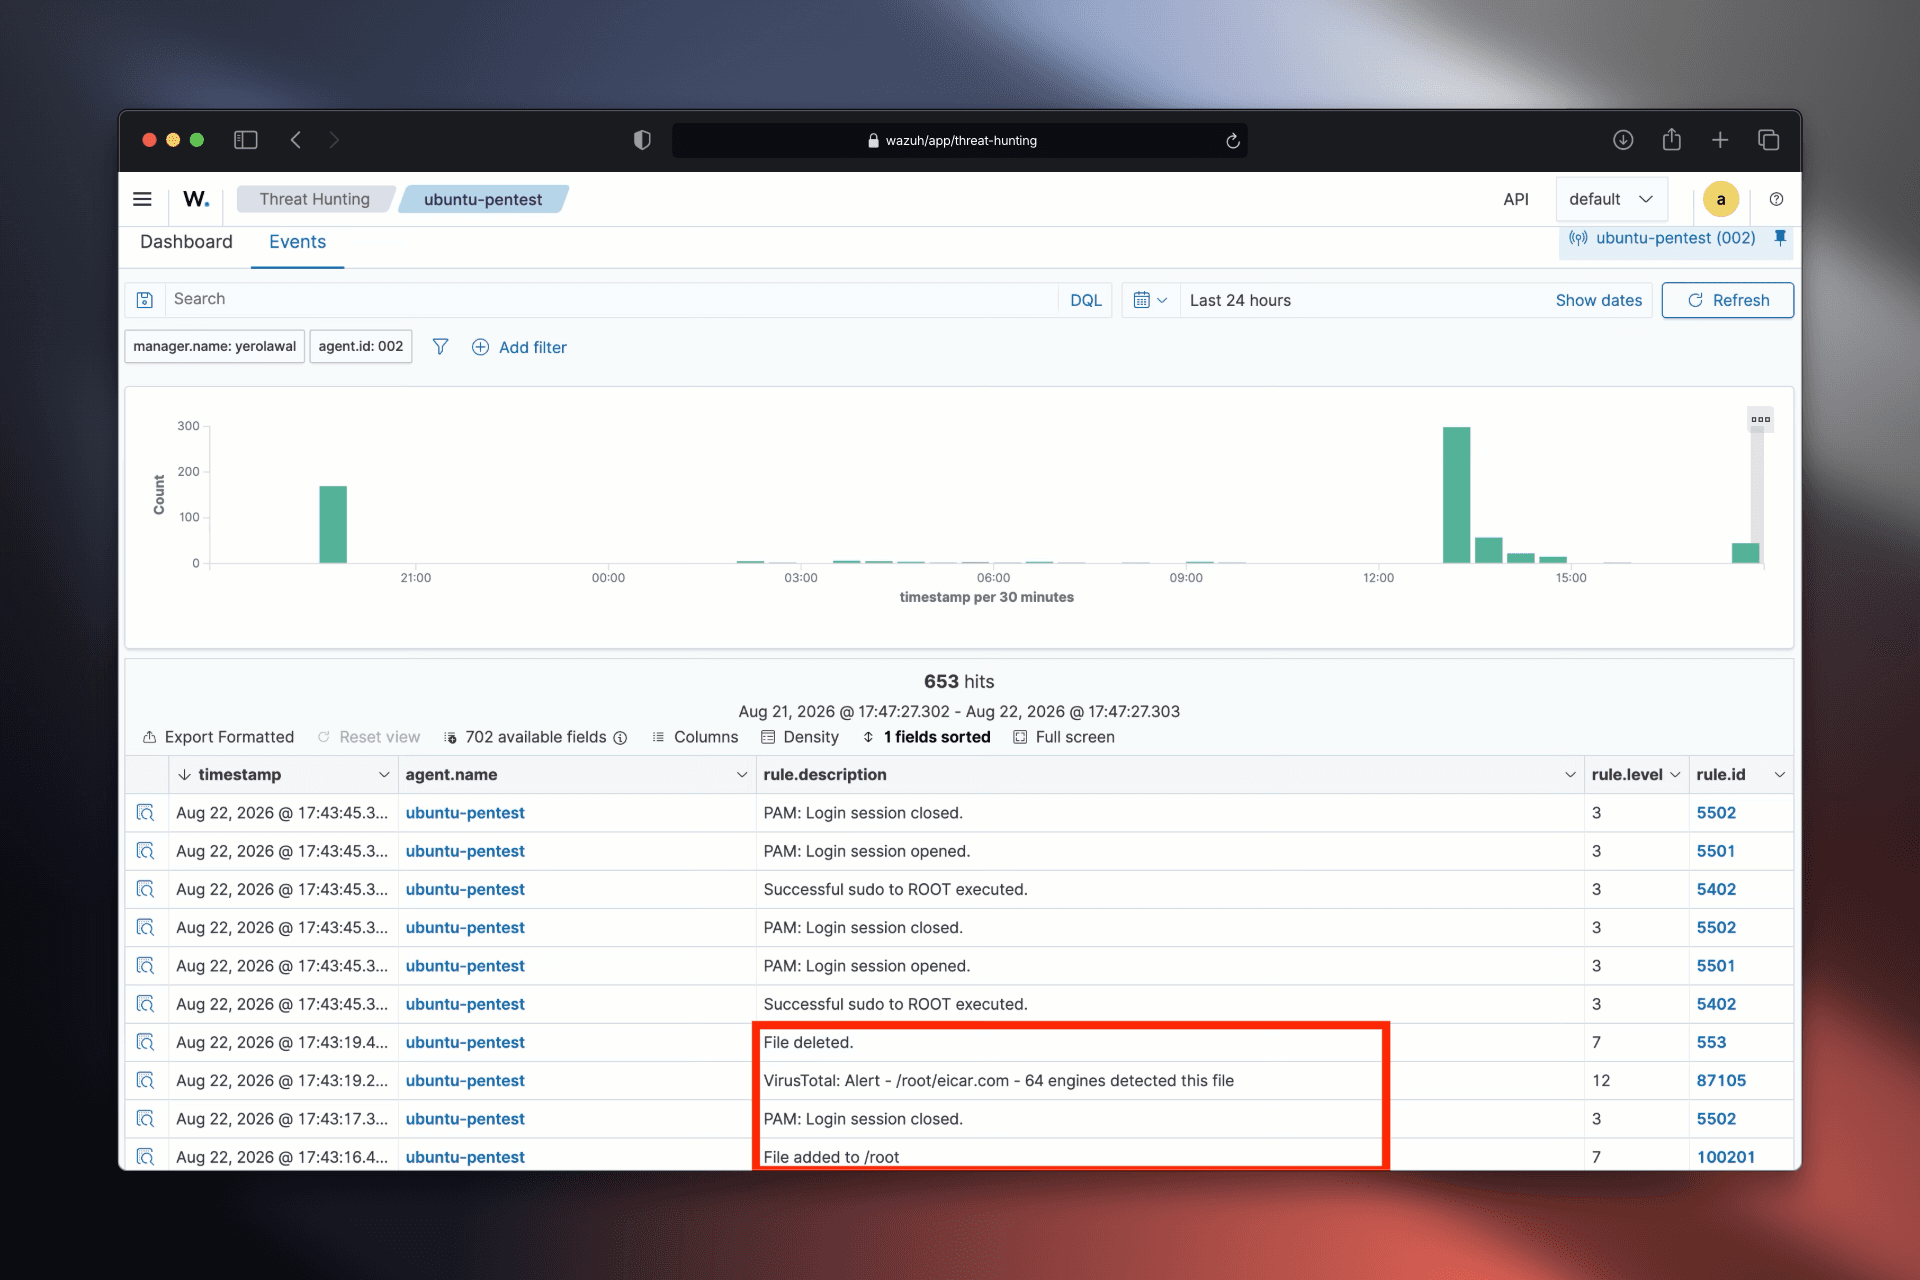 The Detection & SIEM Lab: Catching the Attack with WazuhSelf-hostedMediumWazuh SIEM stack
- 06
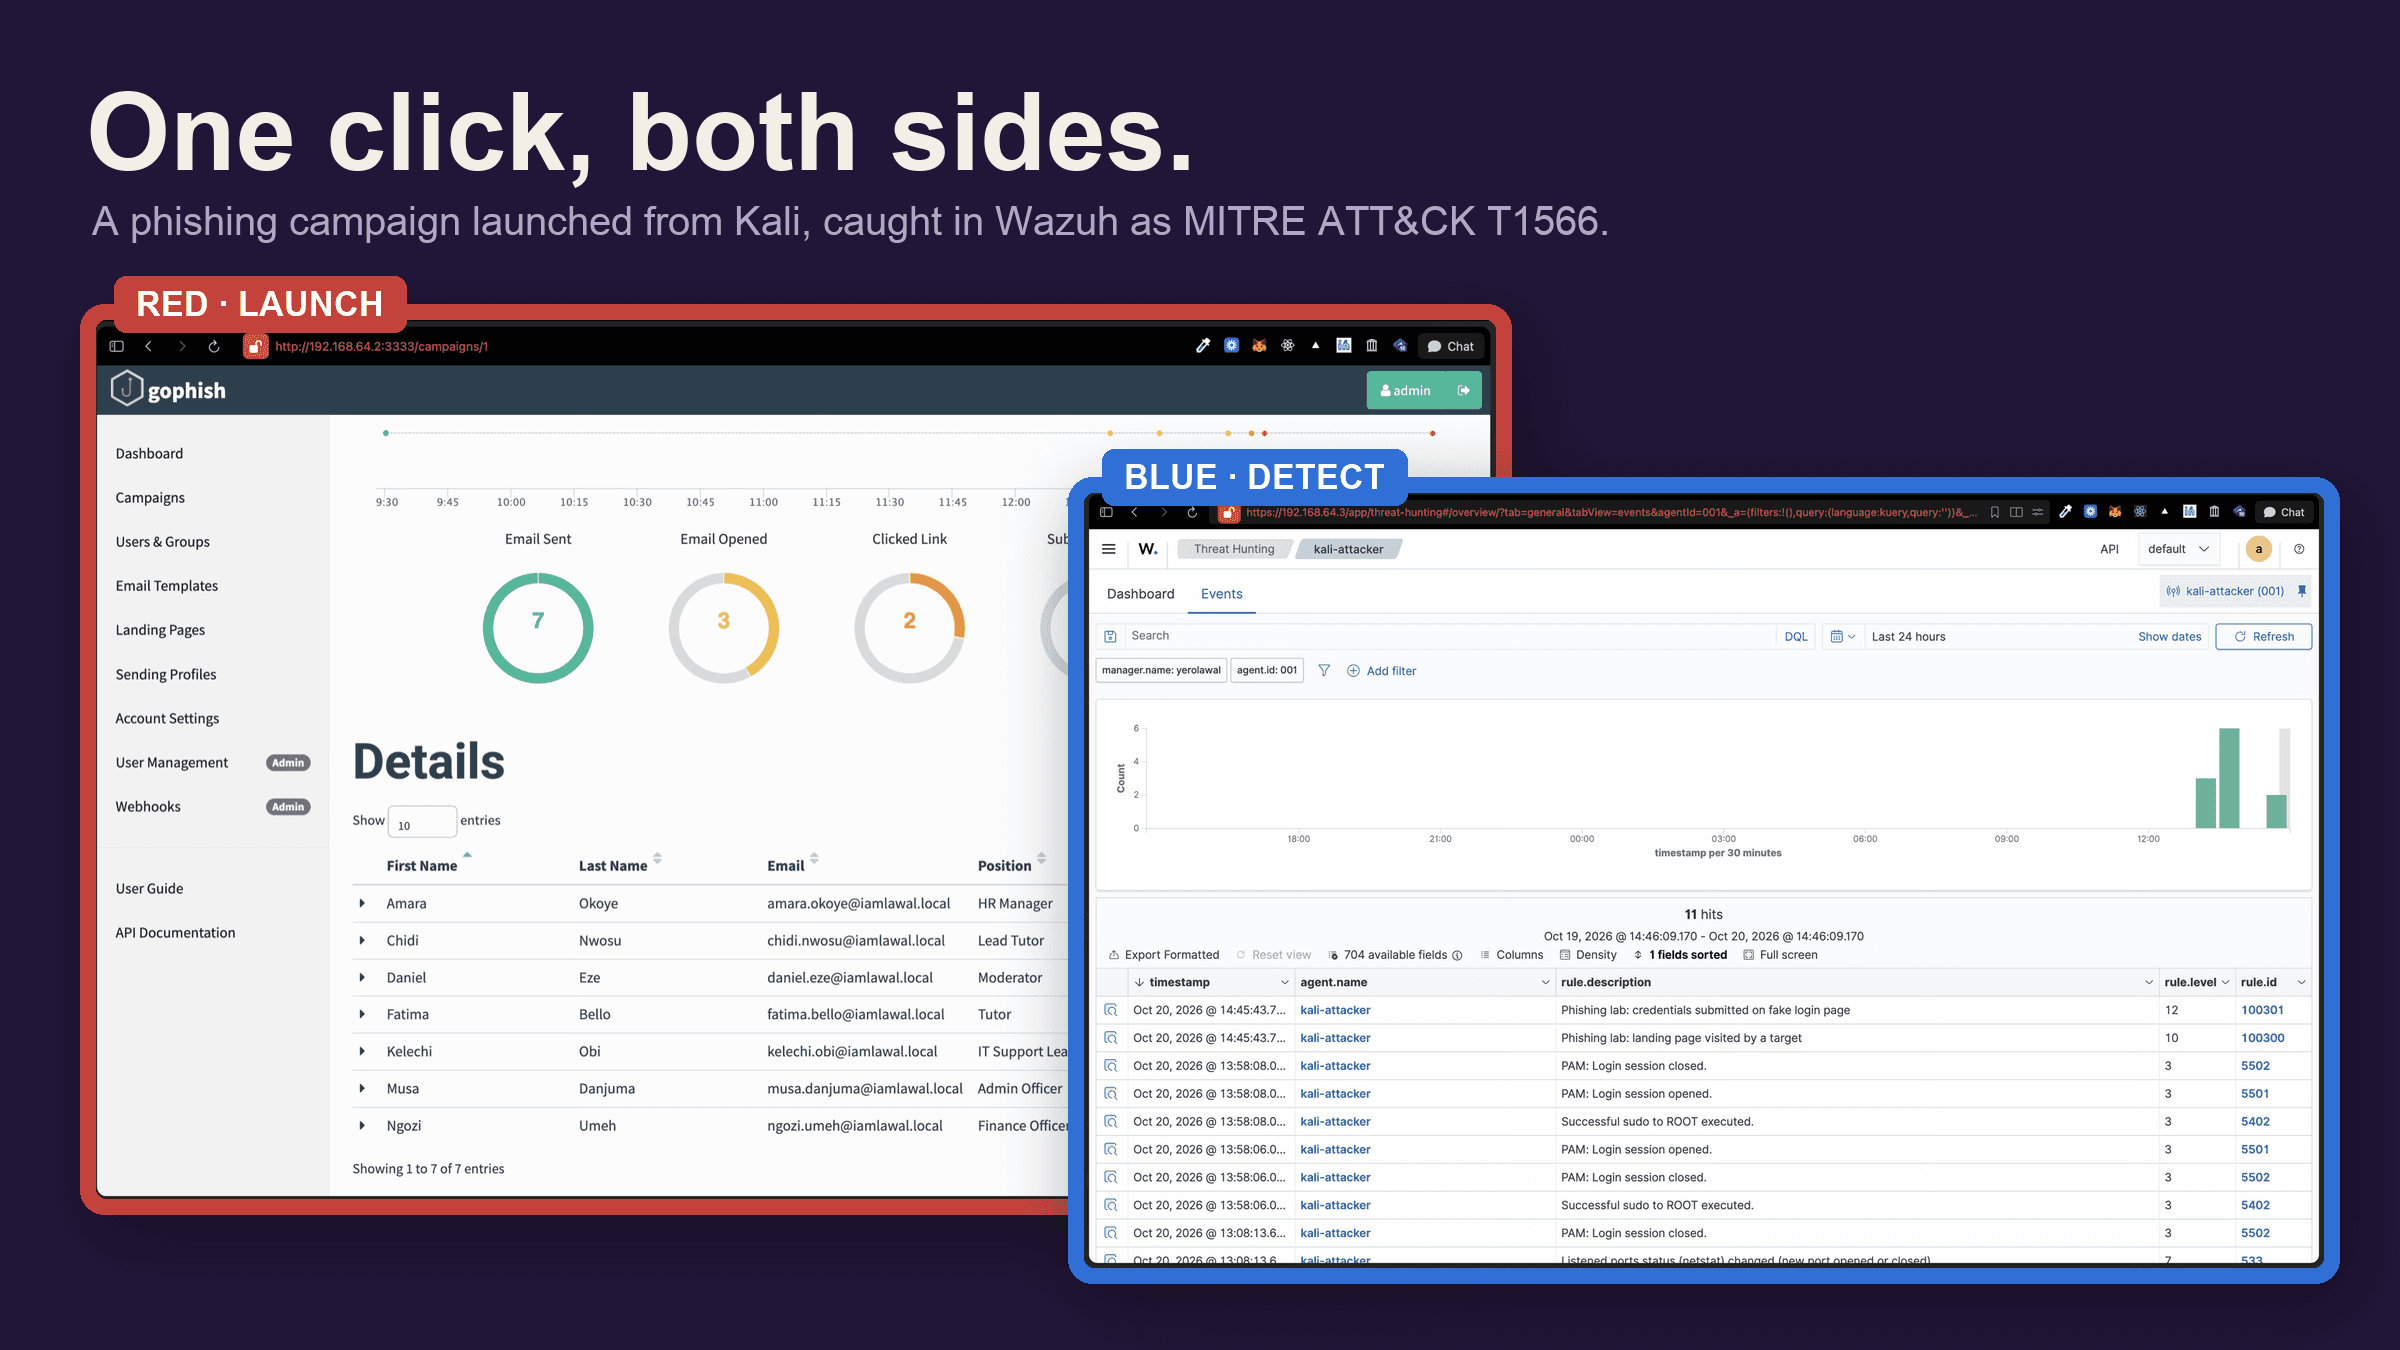 The Phishing Bridge Lab: Run a Campaign, Then Detect ItSelf-hostedMediumGoPhish + Wazuh
Case studies on GitHub
The full record, written up as context, action and result
Threat models, incident analyses, audits, and the CI/CD pipeline and WAF work behind posts here. Each one says what the situation was, what I did, and what came of it.
Open the portfolio on GitHub- 01Application security engineering
- 02Incident analysis
- 03Governance, risk and compliance
- 04Technical skills labs
From the blog
Writing
What the labs taught me, written for the people who build the software rather than the people who attack it.
9 min read
Your coding agent runs as you. So does everything you install into it.
8 min read
A security checklist my coding agent has to run
11 min read
What my WAF actually blocked, and what my app already stops on its own
9 min read
DMARC without breaking your own mail
12 min read
October brought the awareness after all
9 min read