Security / Labs
Labs
A connected set of security labs, not a pile of one-off writeups. The AppSec labs add security to software as it is built, from the build pipeline to the edge to an AI feature. The home labs share one foundation on a single machine, and each track reuses it to go end to end, from recon to root or from attack to alert. Every step names the control that stops it, and the map shows how they fit together.
- Live
- 06
- On the map
- 10
Scroll sideways to see the whole map
6 labs
AppSec labs · Securing what I build
Security added to software as it is built: scanning and a deploy gate at build time, a WAF at runtime, and an AI feature attacked and then contained, each measured rather than assumed.
- Self-hostedMedium14 October 202639 min
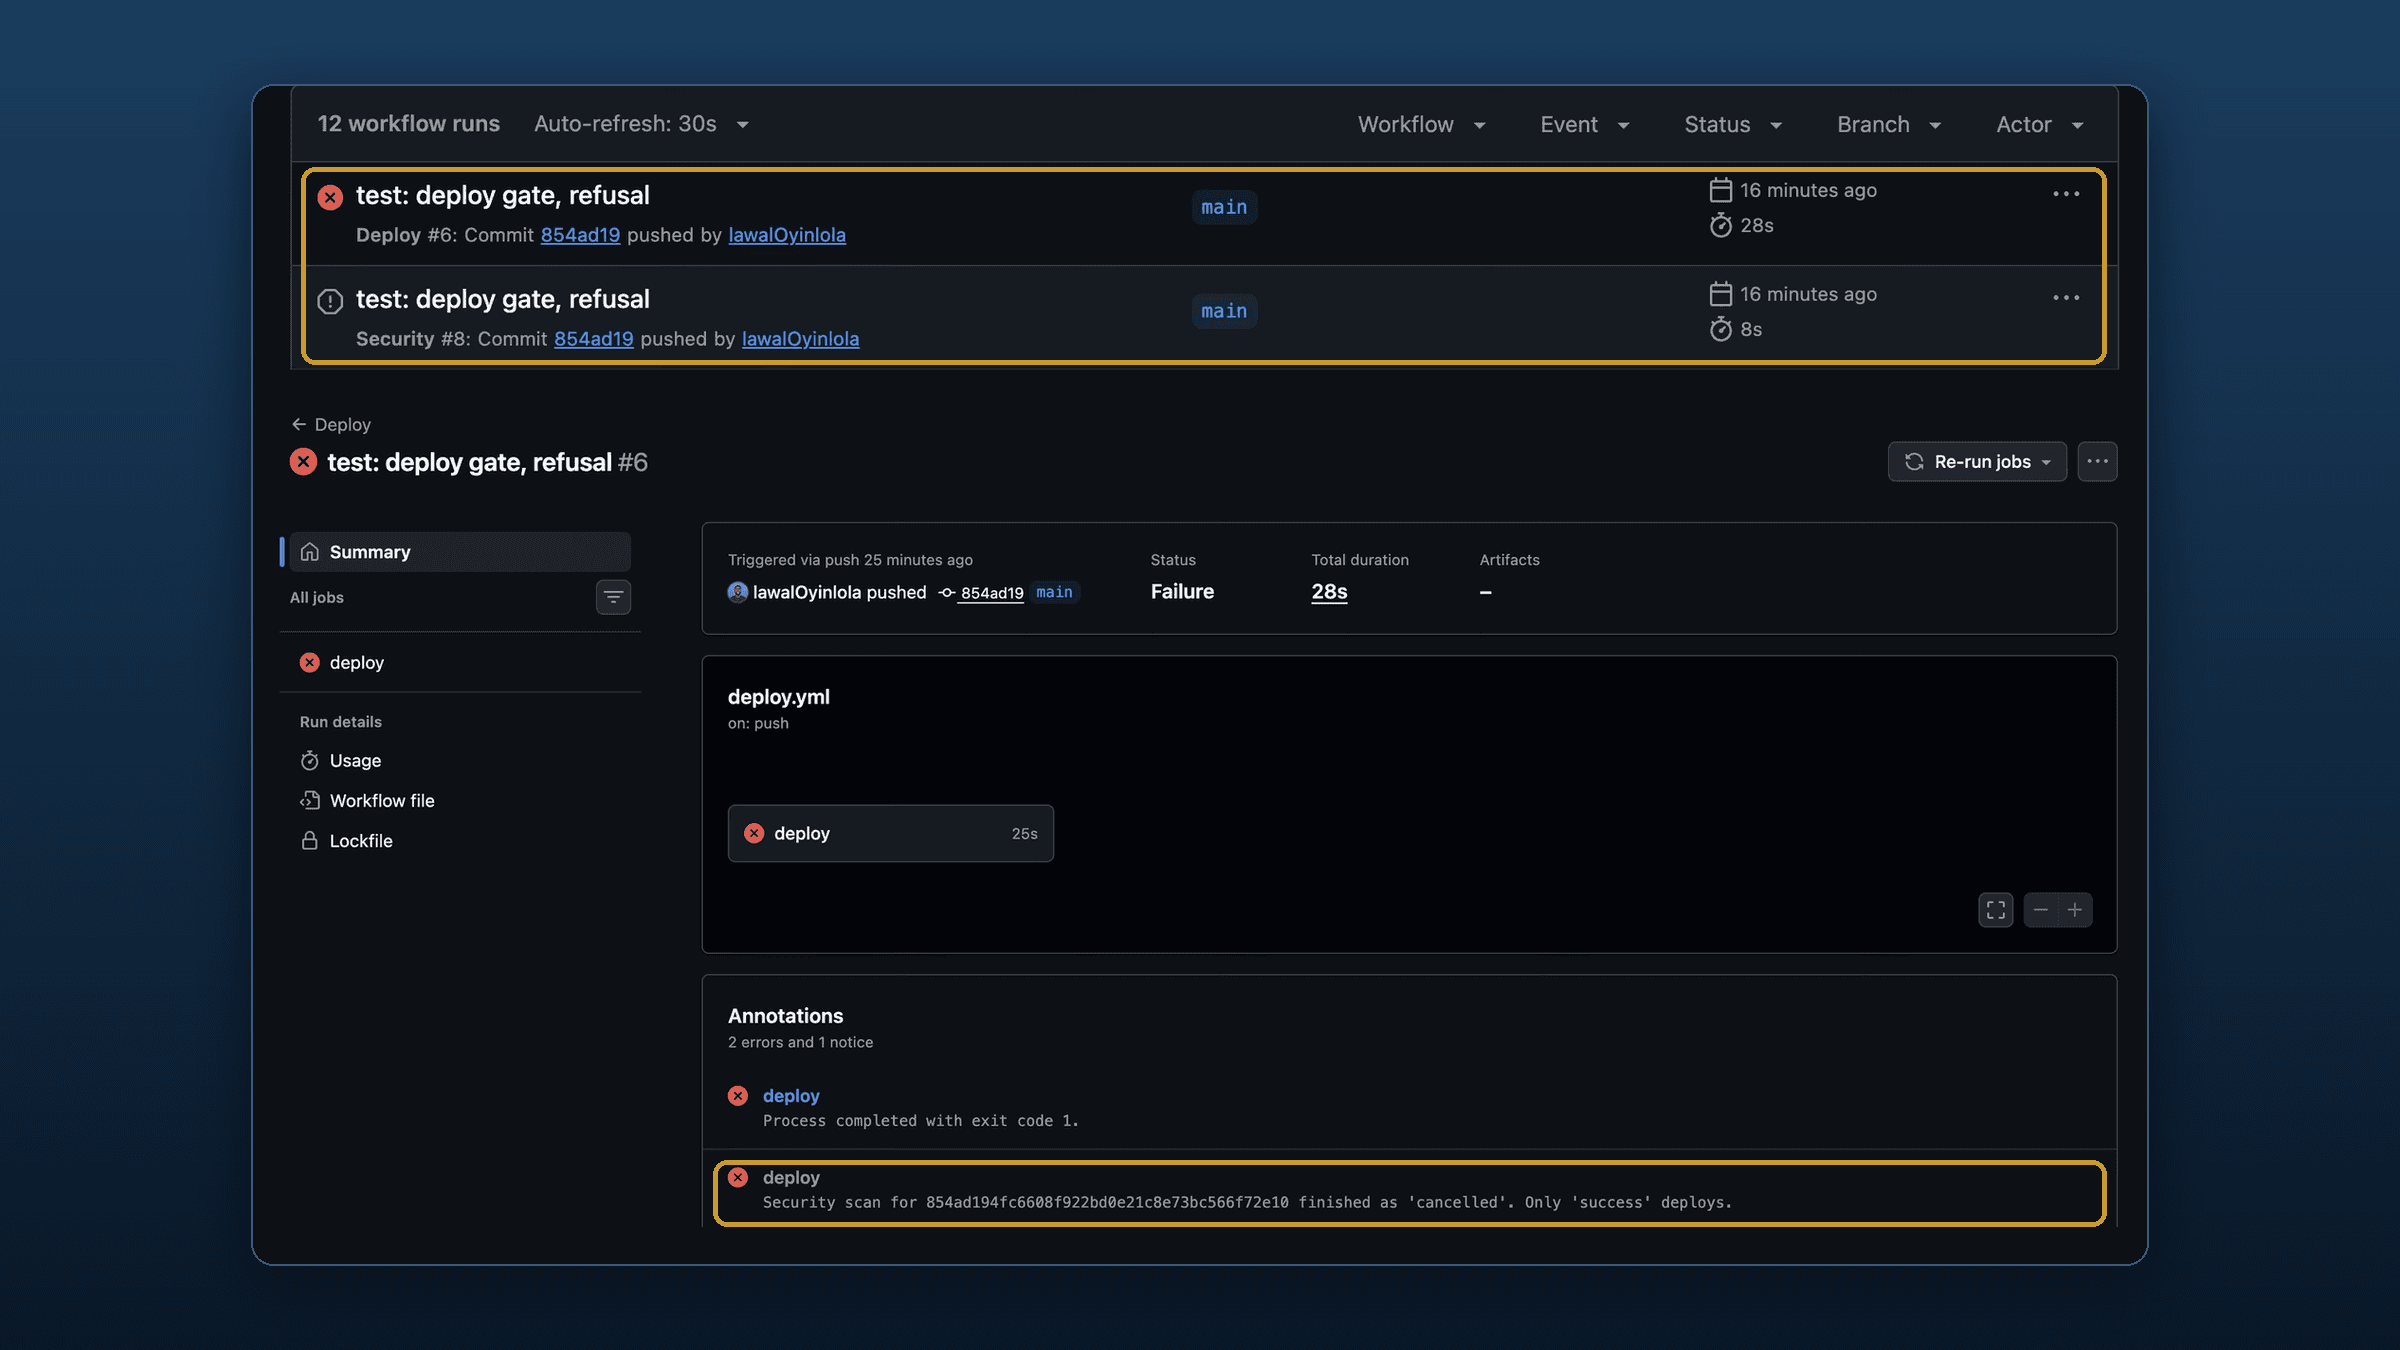
The CI/CD Security Lab: Scanning, Policy and a Deploy Gate That Fails Closed
Target: A Next.js + NestJS web appAdd static analysis, dependency, container and full-history secrets scanning to an app that already ships, set the blocking policy from a measured baseline instead of tool defaults, triage every finding, and gate the deploy so that only an explicit pass gets through.
- Self-hostedMedium16 October 202637 min
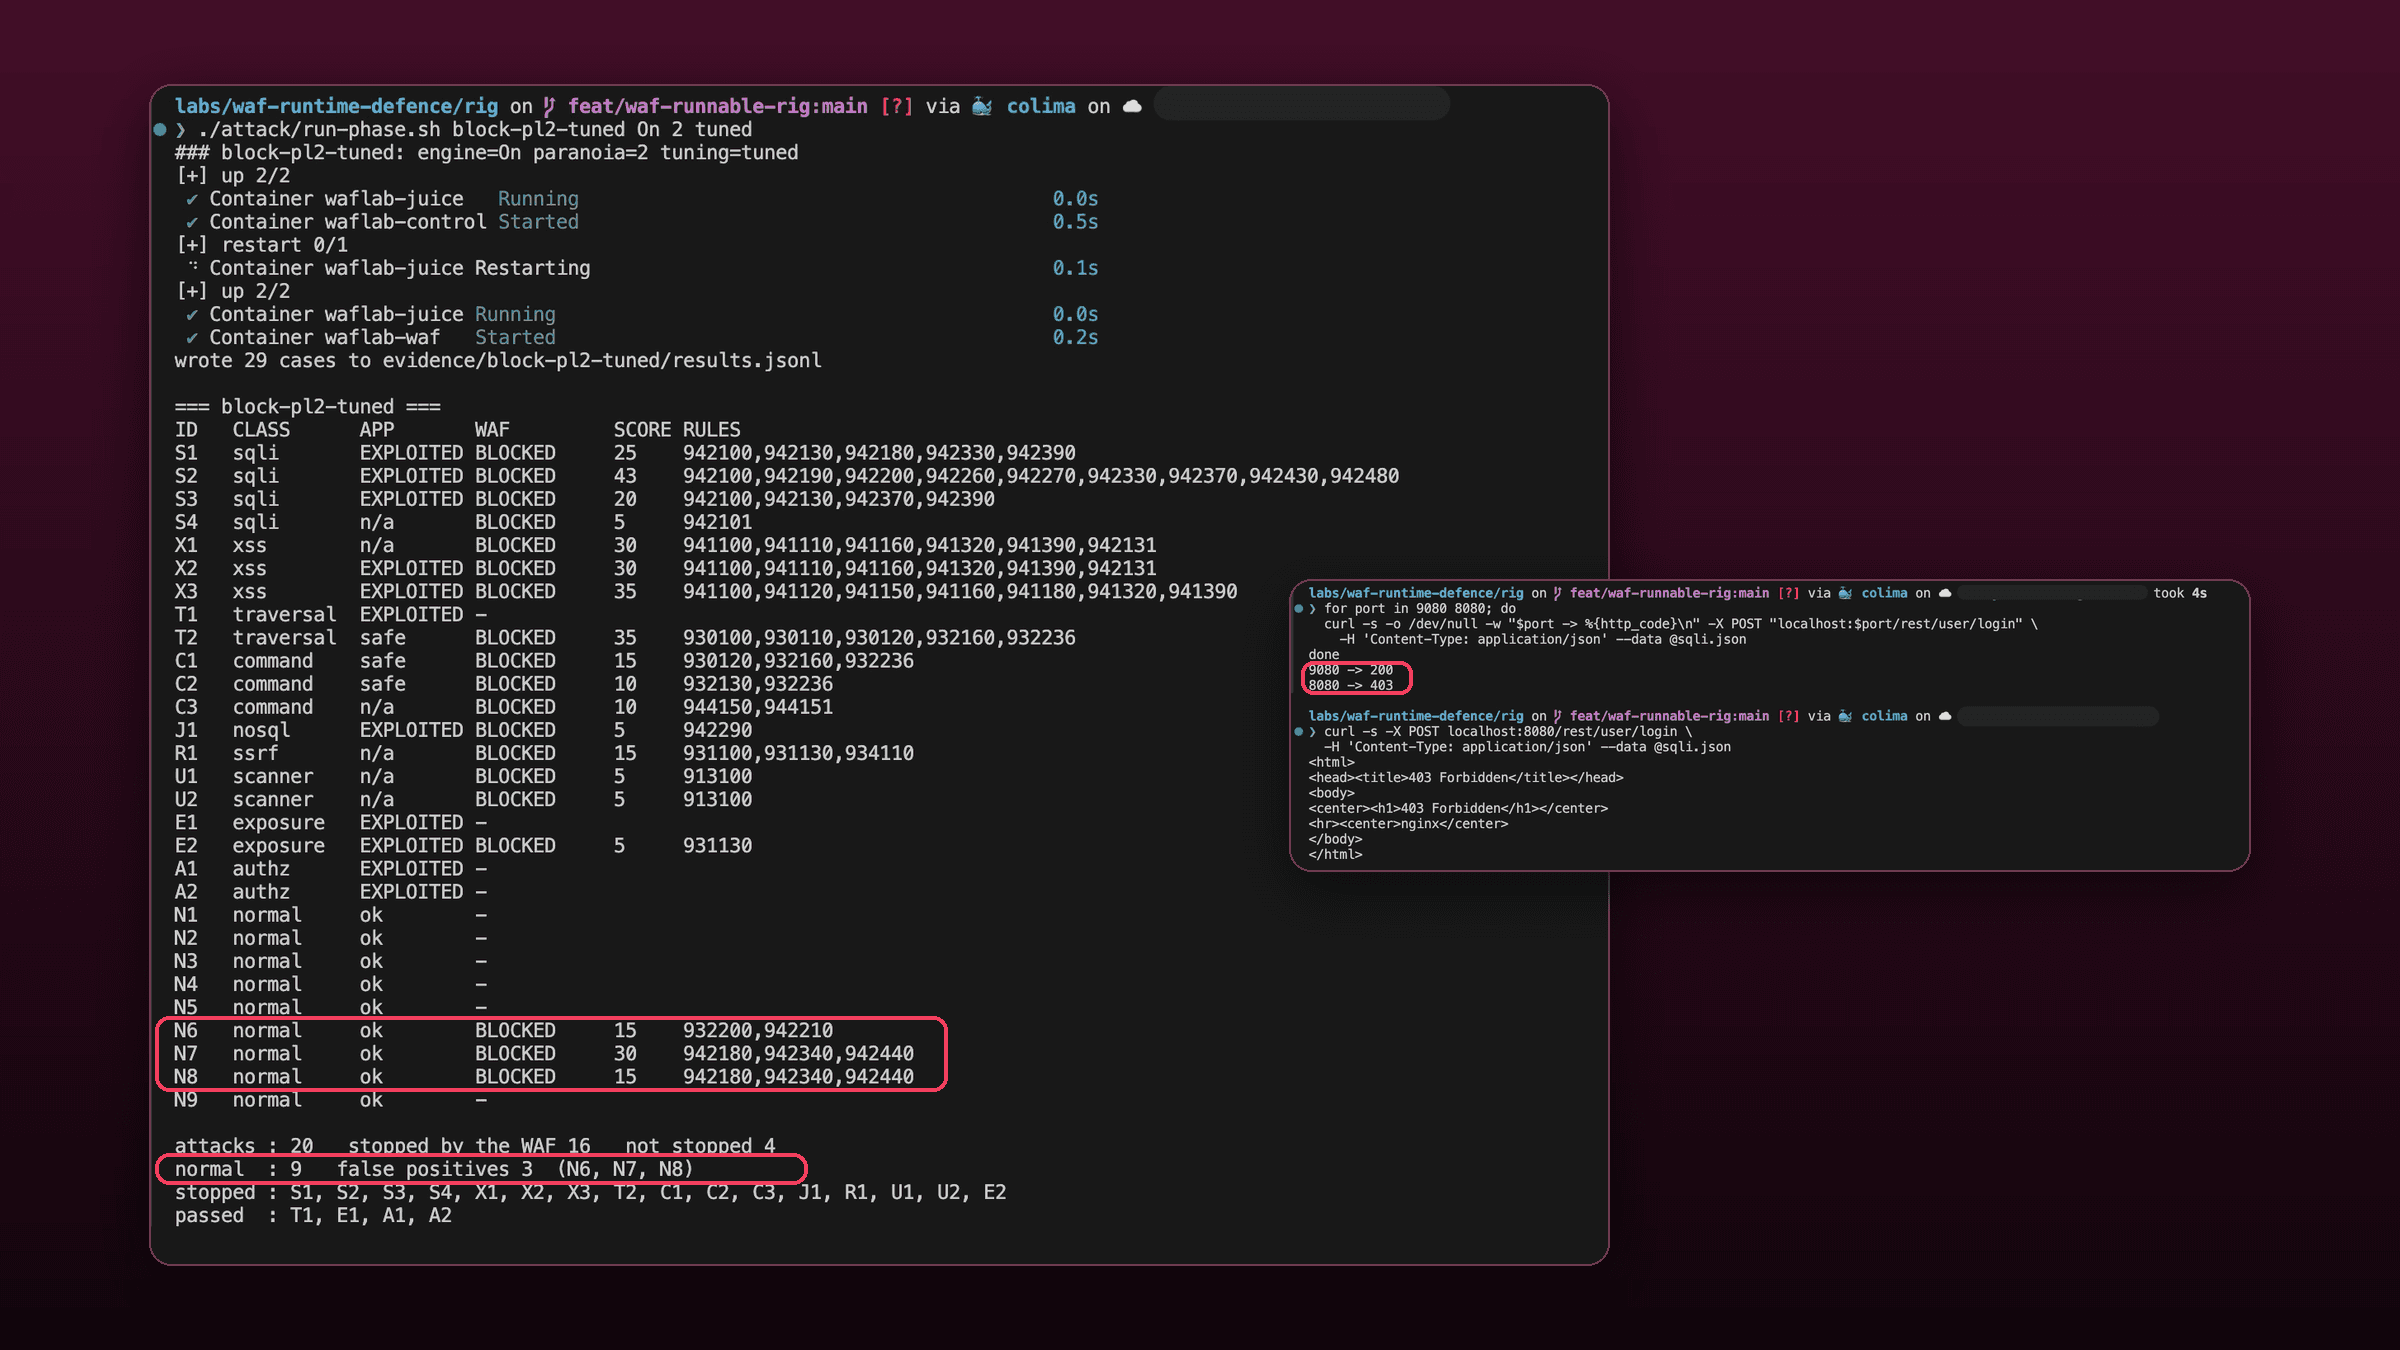
The WAF Lab: ModSecurity and the Core Rule Set, Measured Against a Control
Target: OWASP Juice ShopPut ModSecurity and the OWASP Core Rule Set in front of a deliberately vulnerable app, run 20 attacks and 9 legitimate requests through it with the rule engine off, watching and blocking, then tune it, raise the paranoia level, write a virtual patch, and find the attacks no rule can see.
Local labs · UTM on Apple Silicon
One isolated network on an M-series Mac. A shared foundation, then offensive and defensive tracks that reuse the same boxes.
- Self-hostedEasy1 October 202615 min
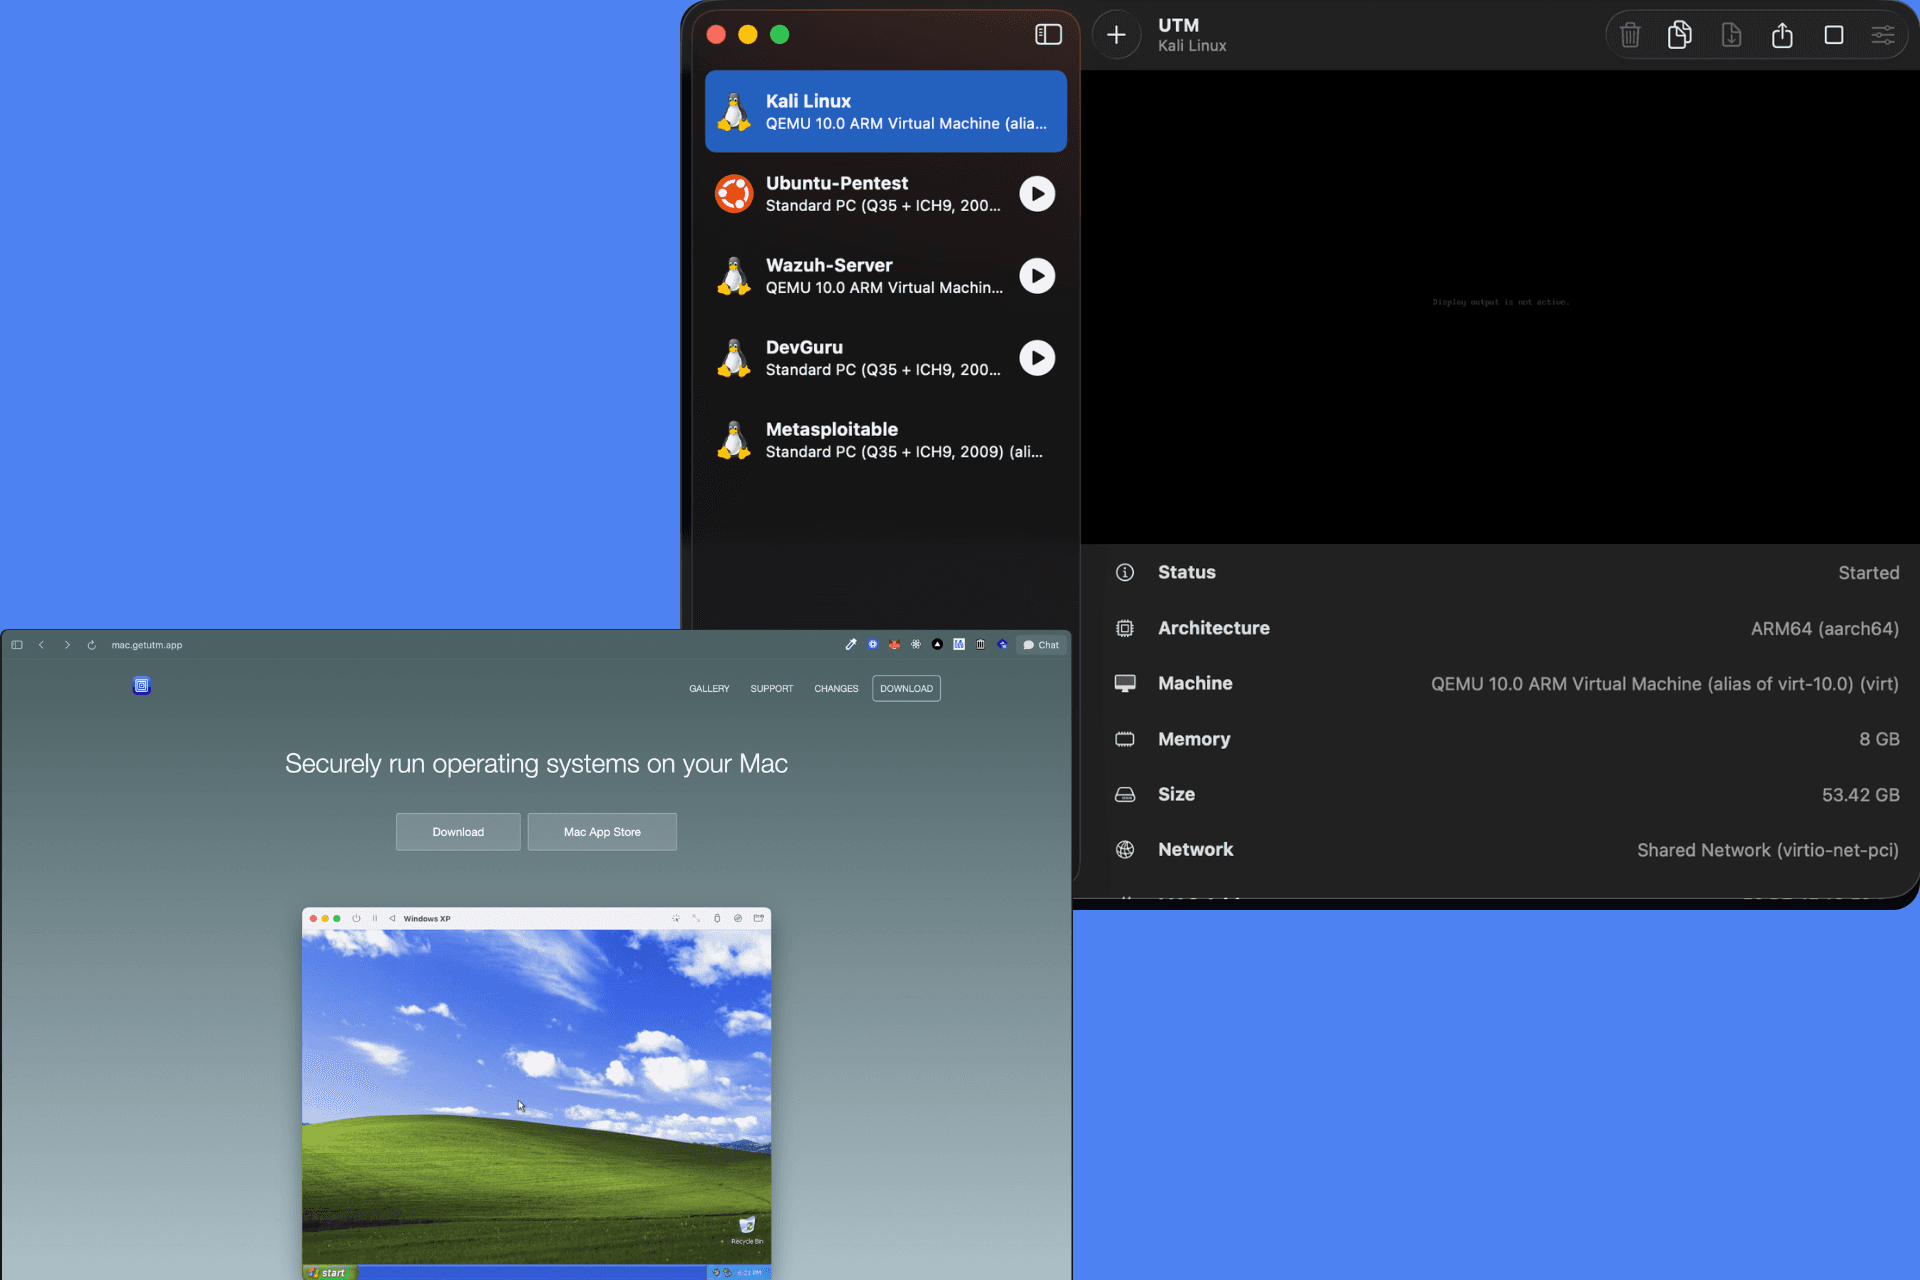
The Foundation Lab: One Security Lab Environment on Apple Silicon
Target: Local VM labThe shared base every lab in this portfolio builds on: UTM on an Apple Silicon Mac, an ARM-native Kali attacker, an Ubuntu Server box for the SIEM, x86 targets under emulation, an isolated network, and snapshots. Set it up once, then branch into any track.
- Self-hostedEasy3 October 202643 min
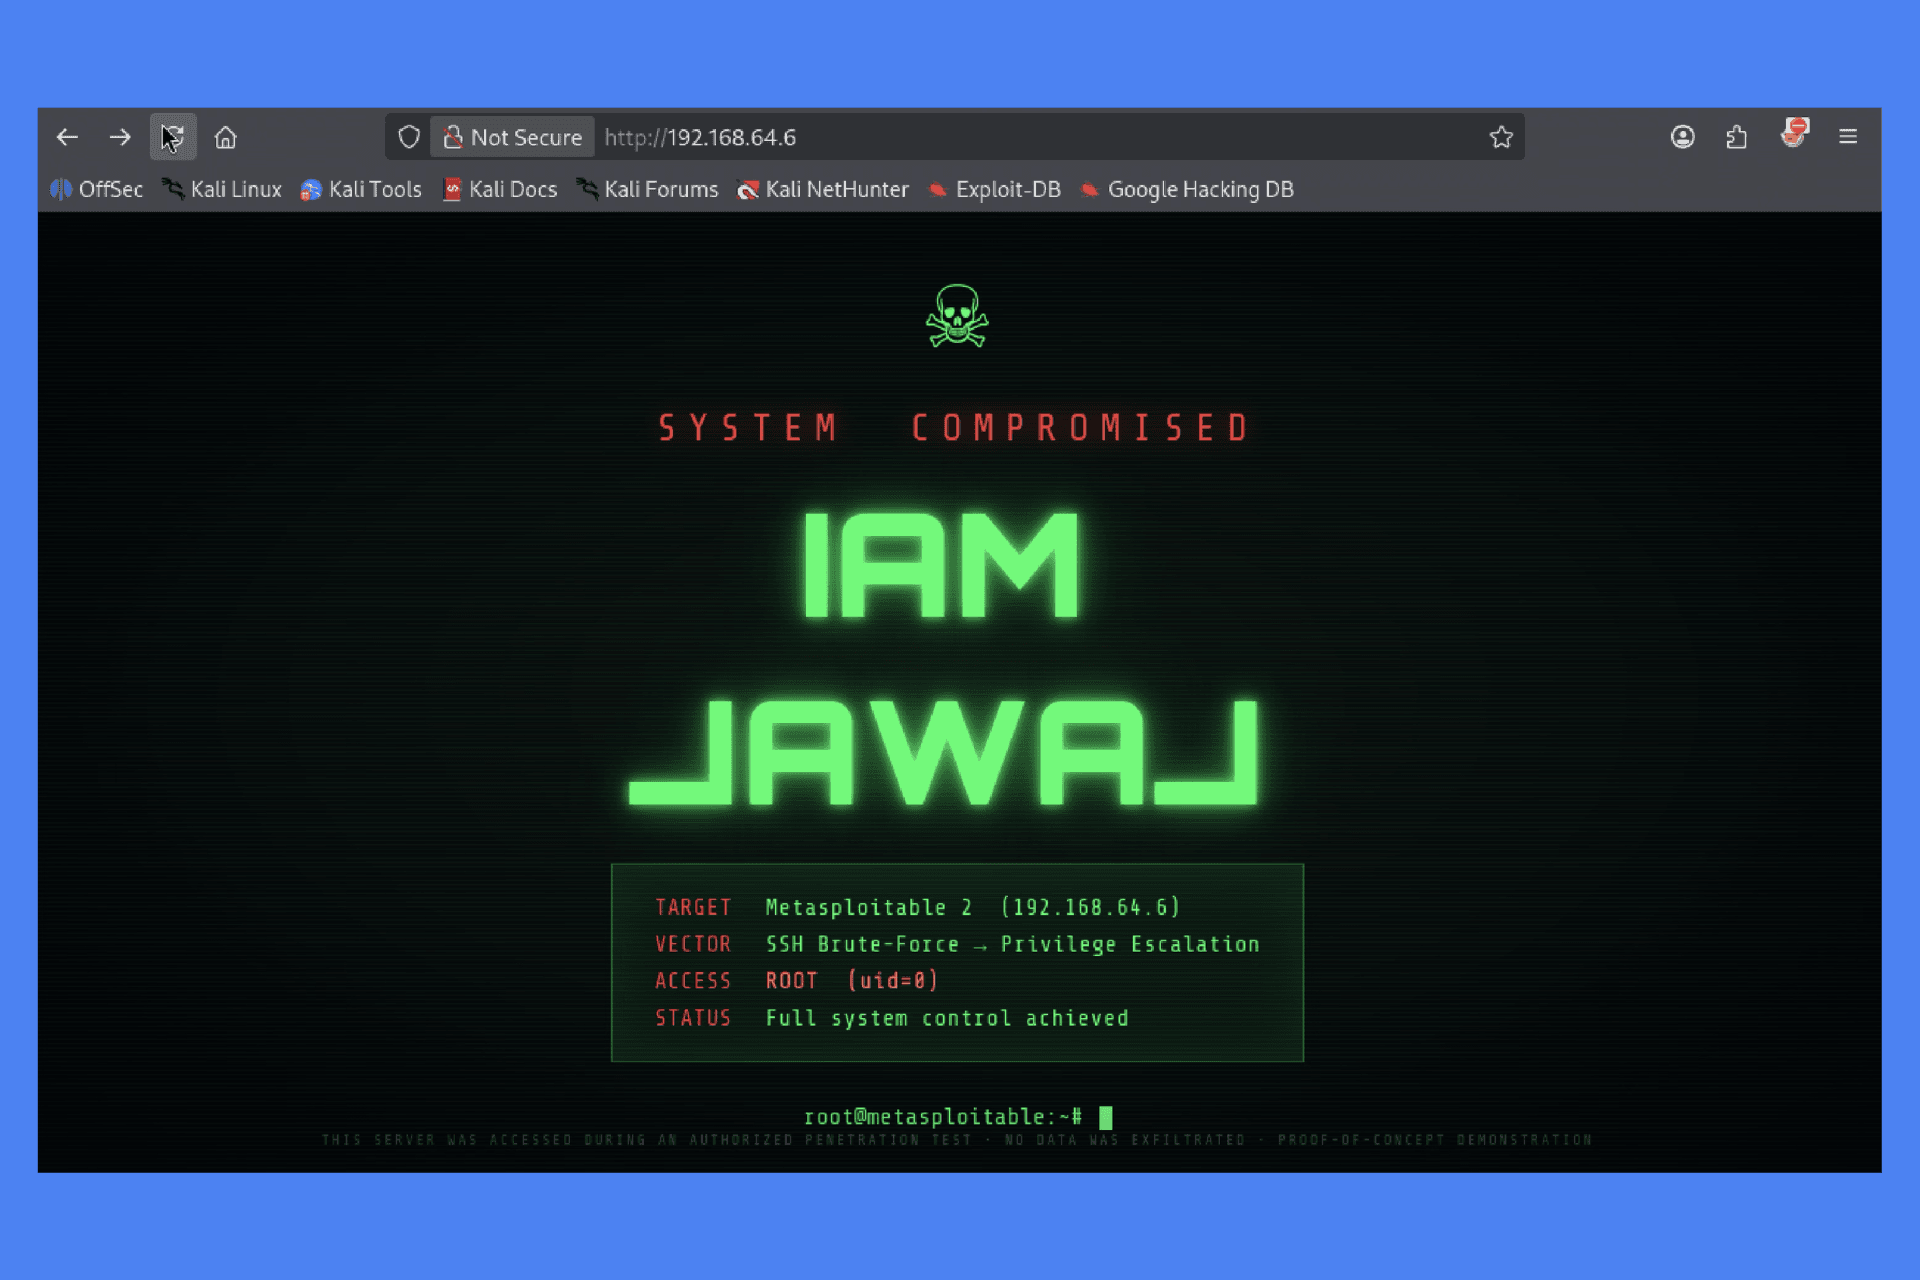
Building a Pentest Lab on Apple Silicon: A Complete Guide
Target: Metasploitable 2A reproducible guide to building a penetration-testing lab on an Apple Silicon Mac with free tools: UTM for the ARM-vs-x86 problem, Kali and Metasploitable 2, vulnerability scanning, two independent paths to root, post-exploitation, and the defensive lesson behind every step.
- Self-hostedMedium5 October 202618 min
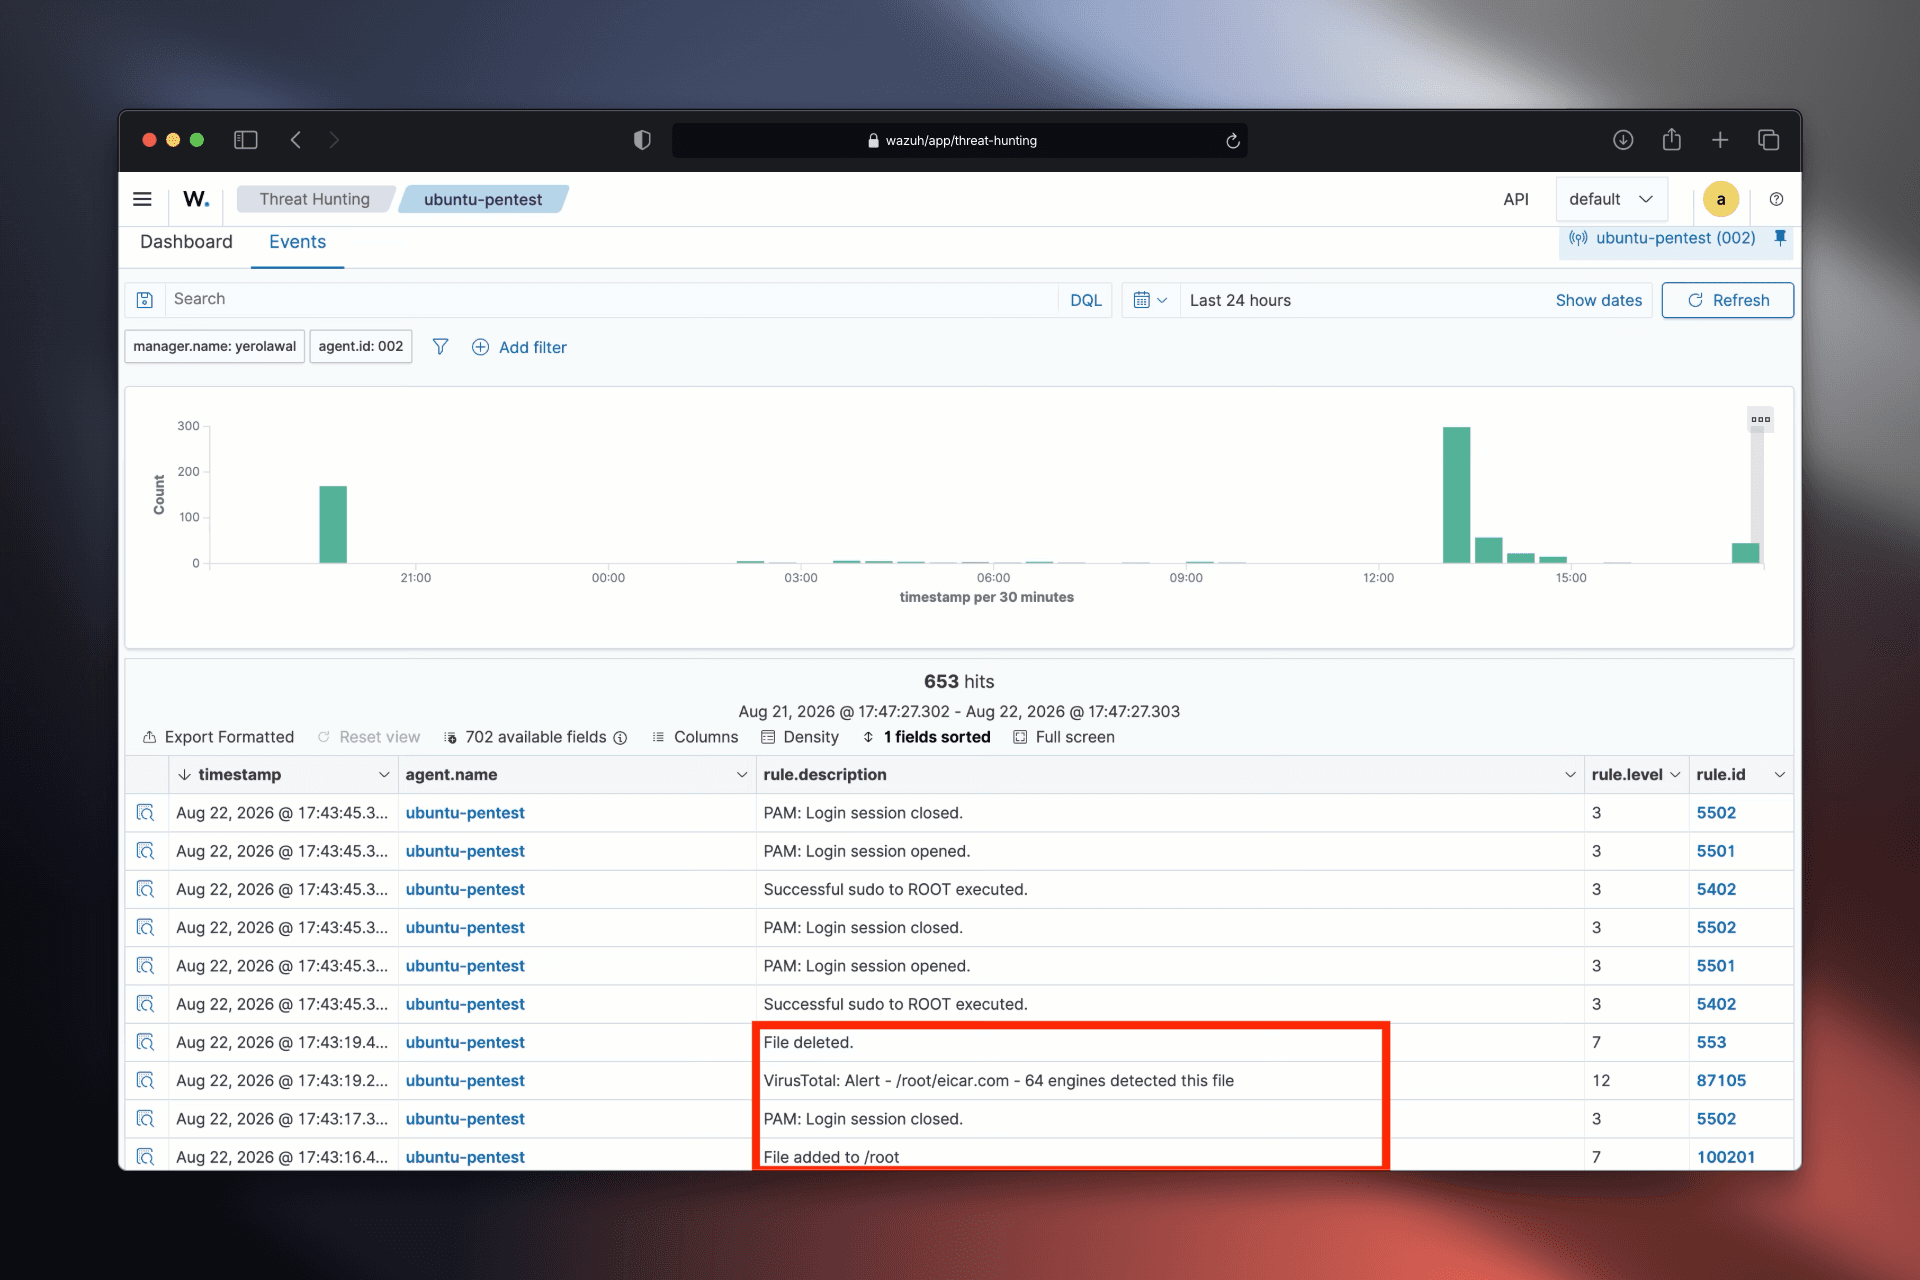
The Detection & SIEM Lab: Catching the Attack with Wazuh
Target: Wazuh SIEM stackThe defensive mirror of the pentest lab: a Wazuh SIEM on the Ubuntu Server box, with agent logs from Kali and the target, Suricata network detection, and VirusTotal file-integrity monitoring. Run the pentest attacks against your own detection and watch one rule auto-delete a malicious file.
- Self-hostedMedium20 October 202624 min
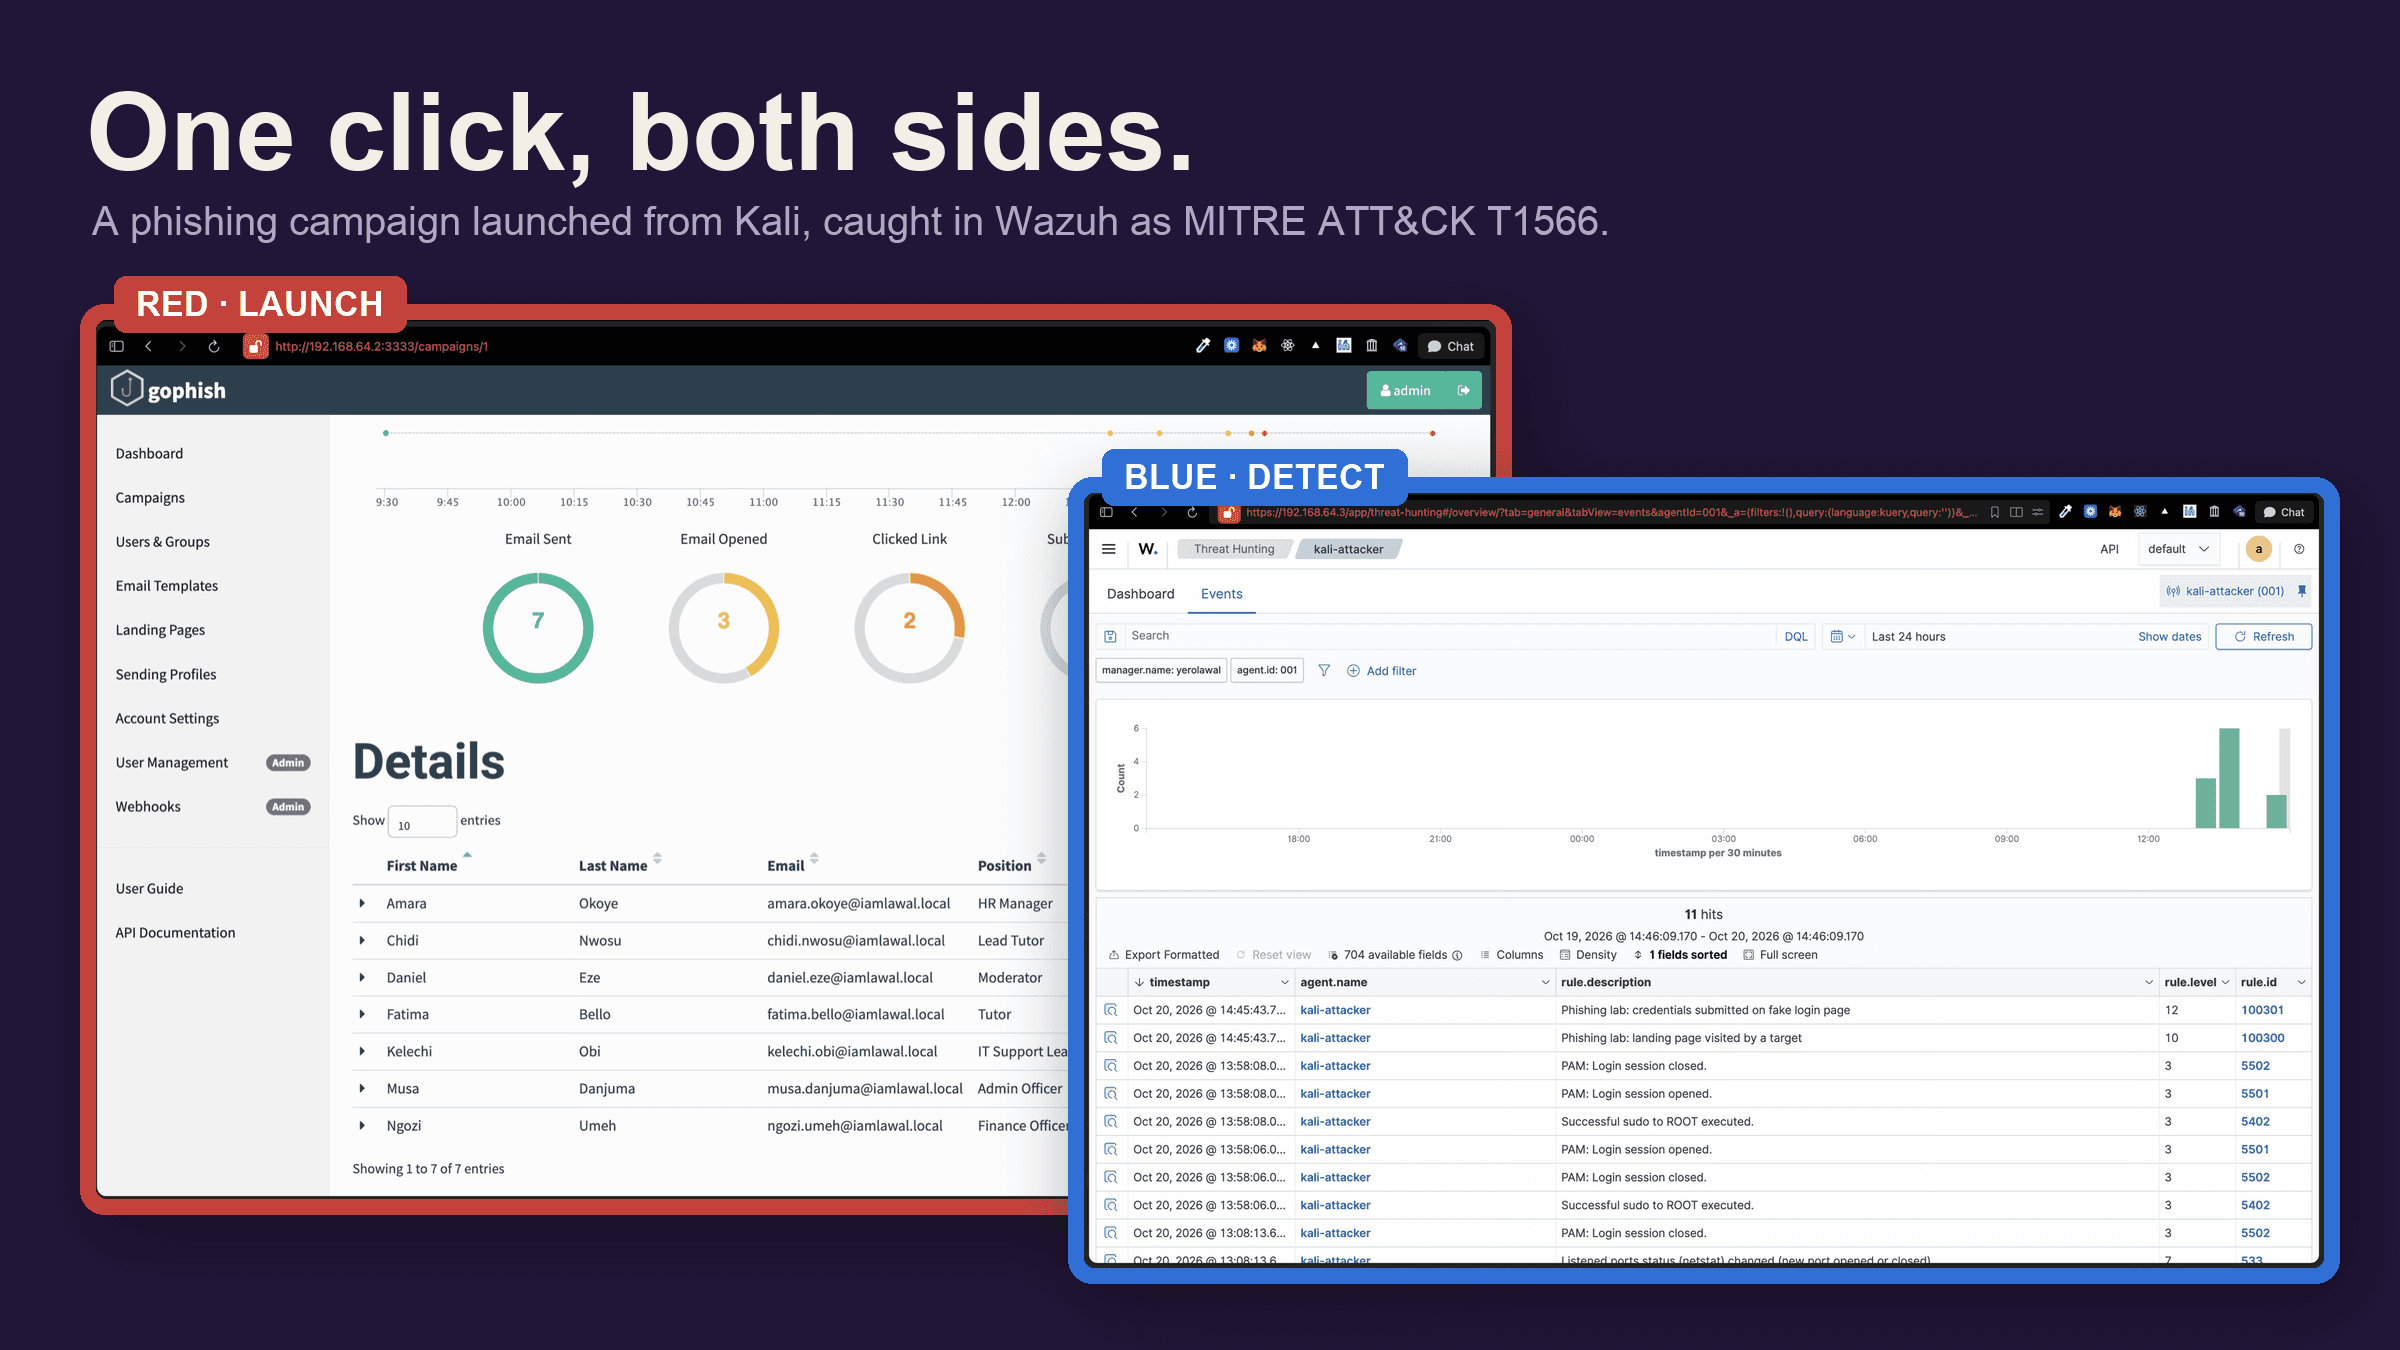
The Phishing Bridge Lab: Run a Campaign, Then Detect It
Target: GoPhish + WazuhA purple-team bridge: build and launch a full phishing campaign on Apple Silicon with GoPhish and Mailpit, click it from a second VM so it crosses the network, then detect the same click with a custom Wazuh decoder and rules mapped to MITRE ATT&CK T1566. No real mail is sent and no real credentials are captured.